


This browser is too old to run Achievable.

Update it, or open this page in a current version of Chrome, Safari, Firefox or Edge. On an iPhone or iPad, update iOS: every browser there runs on the version of Safari that comes with it.

Achievable logoAchievable logo
CCNA
Sign in
Sign up
Purchase
Textbook
Practice exams
Support
How it works
Resources
Exam catalog
Mountain with a flag at the peak
Textbook
Introduction
1. Introduction to networking
2. Administering Ethernet LANs
3. IP connectivity
3.1 Understanding IP addresses
3.2 Calculating networks and hosts (Subnetting)
3.3 Routers and IPv4 routing fundamentals
3.4 Static routing
3.5 Static vs. dynamic routing and OSPF fundamentals
3.6 Router redundancy in an Ethernet LAN using First Hop Redundancy Protocols (FHRPs)
3.7 Configuring Cisco Routers
3.7.1 Initial router configuration and static routes
3.7.2 How to configure OSPFv2 on Cisco routers
4. Network services
5. IPv6
6. Wireless networking
7. Network management and administering network devices
8. Network security fundamentals
9. Network automation and programmability
Wrapping up
Achievable logoAchievable logo
3.7.2 How to configure OSPFv2 on Cisco routers
Achievable CCNA
3. IP connectivity
3.7. Configuring Cisco Routers
Our CCNA course is currently in development and is a work-in-progress.

How to configure OSPFv2 on Cisco routers

17 min read
Font
Discuss
Share
Feedback

Loopback interfaces

Before configuring OSPF, you need to understand a special type of interface called a loopback interface.

A loopback is a logical interface. It doesn’t correspond to a physical port, but it can still be assigned an IP address.

  • On end hosts (Windows, macOS, Linux), the loopback IP address is 127.0.0.1.
  • The main purpose on PCs and servers is to verify that the operating system’s TCP/IP stack is working correctly.

When you ping 127.0.0.1 or run application tests against it, the traffic stays internal to the device. You can think of it as the host “talking to itself” to confirm it can process the layers of the TCP/IP model.

Routers can also have loopback interfaces, but they’re typically used to verify connectivity between routers. The key advantage is stability:

  • A loopback interface stays up as long as the router is up.
  • A physical interface can go down if a cable is disconnected or a link fails.

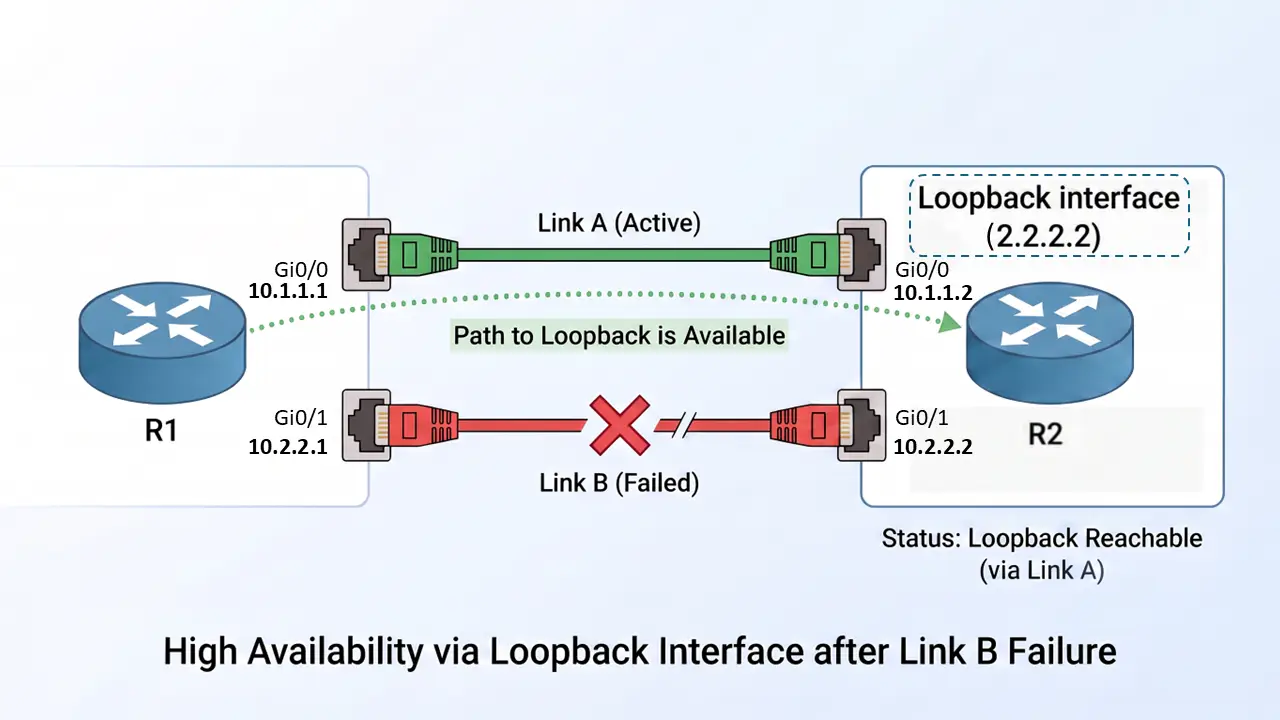
So, if one physical link fails between two routers, you can often still reach the remote router’s loopback interface (as long as you have redundant links and a valid route to that loopback IP).

R1 and R2 connect via two links: Link A (Gi0/0, 10.1.1.1 to 10.1.1.2) active, and Link B (Gi0/1, 10.2.2.1 to 10.2.2.2) failed. R2's loopback interface (2.2.2.2) remains reachable via Link A, so status reads Loopback Reachable (via Link A).
High availability after a link failure using a loopback interface
Achievable
 

Unlike end hosts, routers don’t have loopback interfaces by default. You must create them, and you can create multiple loopbacks on the same router.

To create a loopback interface on a router, go to Global Configuration mode and enter:

interface loopback [loopback #]

Network administrators often use Loopback0 as the first loopback interface, but the number is arbitrary. It’s only used to identify the loopback interface.

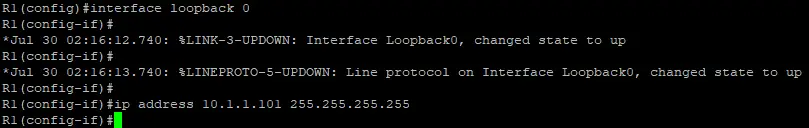
After you create the loopback interface, it will automatically be in the up state (unlike many physical interfaces). While still in Interface Configuration mode, assign it an IP address.

R1 CLI showing creation of interface Loopback0, which comes up with link and line protocol status messages, followed by the command ip address 10.1.1.101 255.255.255.255 assigning that address to the loopback interface.
Creating Loopback0 on R1 and assigning it an IP address
Achievable
 

For the subnet mask, you typically use 255.255.255.255 for a loopback interface. That’s a /32 host address, and it doesn’t represent an entire subnet.

If you haven’t manually configured a routing protocol Router-ID, the IP address on a loopback interface is also used by the router as the routing protocol Router-ID.

Configuring OSPFv2

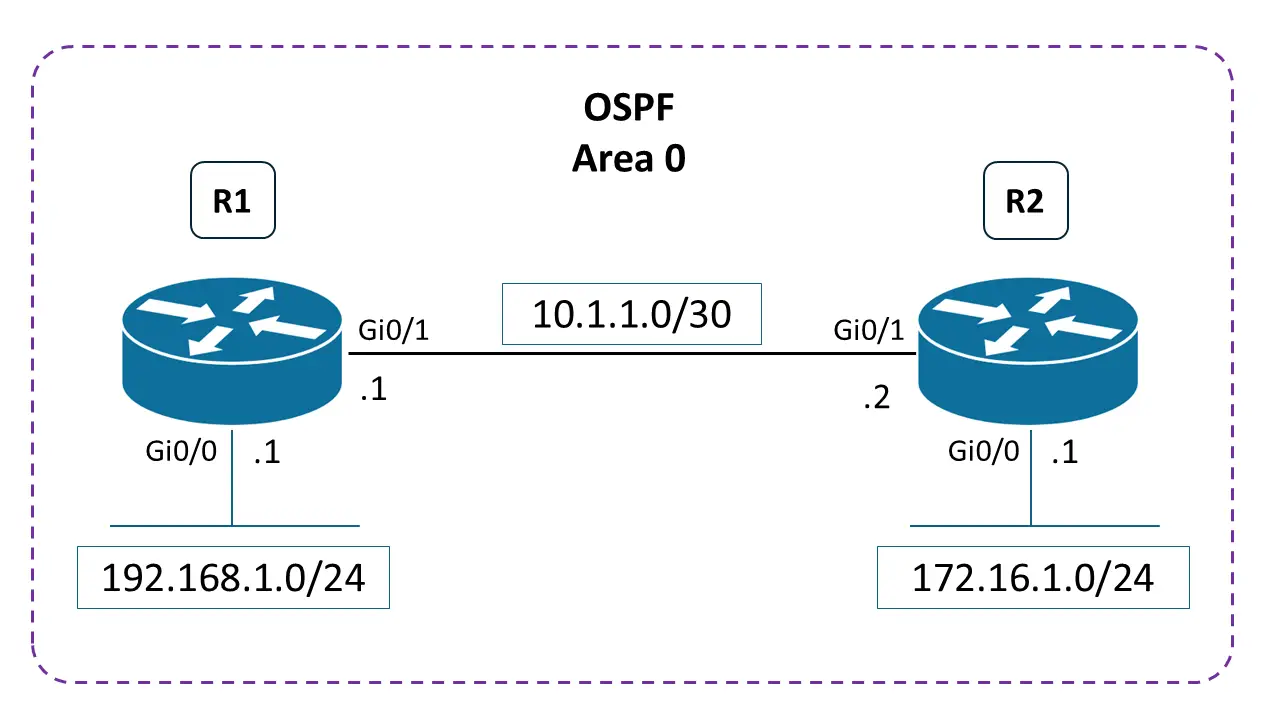
Suppose we want to configure OSPF between two routers connected over a WAN, and each router has a LAN attached.

R1 and R2 are both in OSPF Area 0, linked via Gi0/1 interfaces over 10.1.1.0/30 (R1 .1, R2 .2). R1's Gi0/0 (.1) connects to LAN 192.168.1.0/24, and R2's Gi0/0 (.1) connects to LAN 172.16.1.0/24.
R1 and R2 with their OSPF networks
Achievable
  • R1 is connected to the 192.168.1.0/24 network.
  • R2 is connected to the 172.16.1.0/24 network.
  • The link between the routers uses the 10.1.1.0/30 network.

R1 and R2 want to advertise their directly connected LANs to each other using OSPF.

First, enter Global Configuration mode and enable the OSPF process. We’ll use a Process ID of 1.

The OSPF Process ID is arbitrary and locally significant. It is not advertised to the other router.

router ospf 1

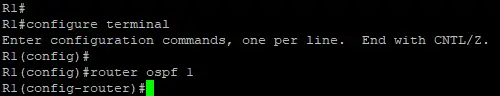
This puts you into Routing Protocol Configuration mode, and the prompt changes to:

R1(config-router)#

Router CLI on R1: entering configure terminal, then the command router ospf 1, which moves the prompt to R1(config-router)#.
Configuring OSPF on R1
Achievable

OSPF router-ID selection

After enabling OSPF, the router must have an OSPF Router-ID. There are three ways the Router-ID can be selected.

A Router-ID is a 32-bit value written in dotted-decimal notation. It doesn’t have to be an IP address that actually exists on the router.

You can manually configure the OSPF Router-ID under the router ospf configuration mode using:

router-id x.x.x.x

Here, “x.x.x.x” is the Router-ID.

For example, to configure a Router-ID of “10.1.1.1” on R1:

R1(config)#configure terminal R1(config-router)#router ospf 1 R1(config-router)#router-id 10.1.1.1

However, if you don’t manually specify the Router-ID, then the router will use a Loopback interface with the highest IPv4 address out of all loopback interfaces. If no loopback interfaces exist, it will select the router interface with the highest IPv4 address out of all router interfaces.

The Router-ID selection process can be summarized like this, in order of precedence:

  1. Select the Router-ID that was manually configured (router-id [x.x.x.x]).
  2. If a Router-ID is not manually configured, then select the Loopback interface with the highest IPv4 address out of all the Loopback interfaces on the Router.
  3. If there are no Loopback interfaces on the Router, select the router interface with the highest IPv4 address out of all the router interfaces configured with IPv4 addresses.

Without the Router-ID, the OSPF process on the router cannot function.

Influencing the OSPF DR/BDR selection

In Chapter 3.7 OSPF neighbor adjacencies, we discussed that the OSPF interface priority is the first method used to determine which router becomes the DR during the DR/BDR election (part of the OSPF broadcast adjacency process).

  • The router with the highest OSPF interface priority becomes the DR.
  • The router with the second-highest interface priority becomes the BDR.

To configure the OSPF interface priority, enter Interface Configuration mode on the interface that will form the OSPF adjacency, then use:

ip ospf priority [0-255]

The OSPF Priority value ranges from 0-255. Setting the OSPF Priority value to 255 using the “ip ospf priority 255” command underneath a router interface ensures that the Router will be the DR for any OSPF adjacency that it forms on that router interface, because it’s the highest value.

Setting the OSPF Priority value to 0 using the “ip ospf priority 0” command disables the router interface from participating in a DR/BDR election, meaning, it would never become the DR or BDR for any OSPF adjacencies that it would form on that router interface.

Example: set the OSPF interface priority to 255 on GigabitEthernet0/0 so it always becomes the DR on that segment:

interface gigabitethernet0/0 ip ospf priority 255

If the OSPF priority ties between routers, the router with the highest Router-ID becomes the DR. The router with the second-highest Router-ID becomes the BDR, and it takes over as DR only if the current DR fails.

Next, we need to form the adjacency between the two routers by enabling OSPF on the router interfaces (see Chapter 3.7 OSPF neighbor adjacencies). To enable OSPF on interfaces, we configure network statements.

Network statements and wildcard masks

A network statement tells the routing protocol which router interfaces should participate in the routing process.

Here’s what happens when a router interface matches a network statement in OSPF:

  • OSPF is enabled on that interface.
  • The router starts sending OSPF Hellos out that interface.
  • The router creates LSAs for the directly connected network on that interface.
  • After an adjacency forms, those LSAs can be advertised to the OSPF neighbor.

OSPF network statements are structured like this:

Command Network of the router interface Wildcard Mask OSPF Area ID


To configure a network statement, you also need to understand the wildcard mask.

We will discuss wildcard masks in more detail in a later chapter.

A wildcard mask is the inverse of a subnet mask. It defines the range of IP addresses that an interface can fall within to match the network statement.

To derive a wildcard mask from a subnet mask, subtract the subnet mask from 255.255.255.255.

Example #1: wildcard mask for subnet mask 255.255.255.0 (/24):

255.255.255.255

0.0.0.255−255.255.255.0​

The wildcard mask is 0.0.0.255.


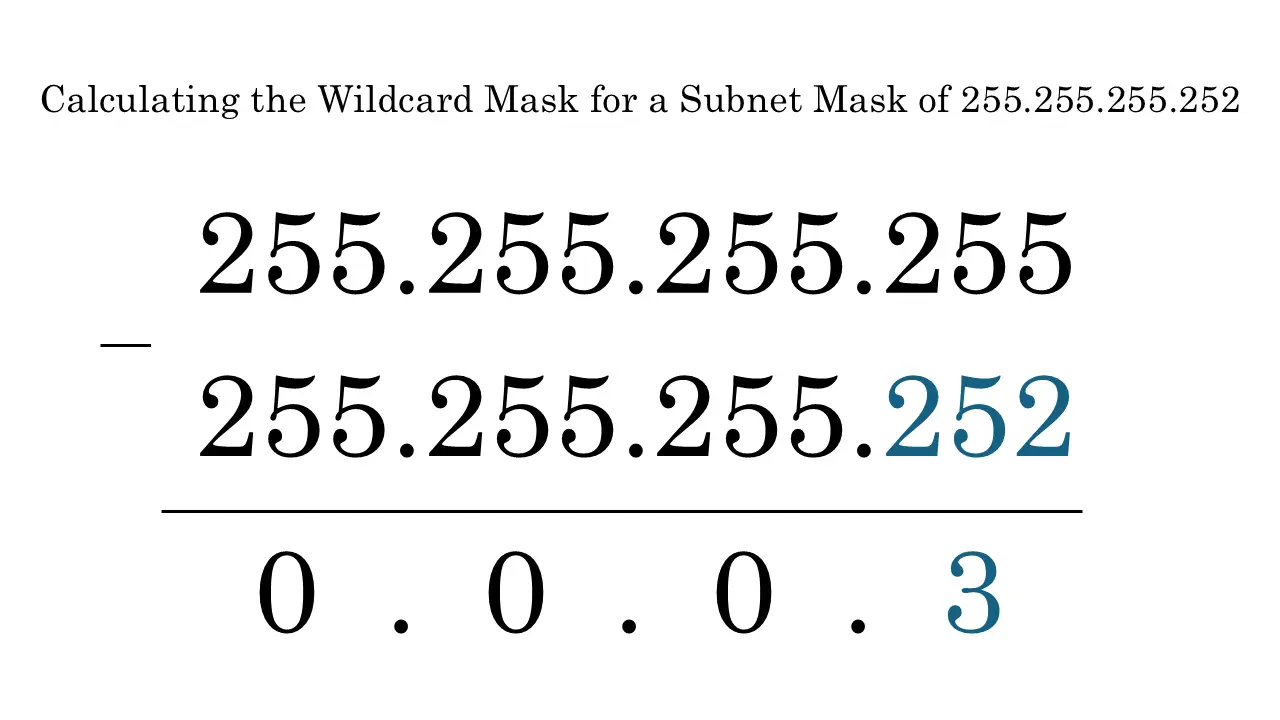
Example #2: wildcard mask for subnet mask 255.255.255.252 (/30):

Subtracting subnet mask 255.255.255.252 from 255.255.255.255, octet by octet, gives the wildcard mask 0.0.0.3.
Calculating the wildcard mask for 255.255.255.252
Achievable
 

The wildcard mask is 0.0.0.3.

Now we can enable OSPF on the two router interfaces on R1 by entering these commands under OSPF Routing Protocol Configuration mode:

Command Network of the router interface Wildcard Mask OSPF Area ID
network 192.168.1.0 0.0.0.255 area 0
network 10.1.1.0 0.0.0.3 area 0

That is:

router ospf 1 network 192.168.1.0 0.0.0.255 area 0 network 10.1.1.0 0.0.0.3 area 0 end

We must also do the same thing on R2:

Command Network of the router interface Wildcard Mask OSPF Area ID
network 172.16.1.0 0.0.0.255 area 0
network 10.1.1.0 0.0.0.3 area 0

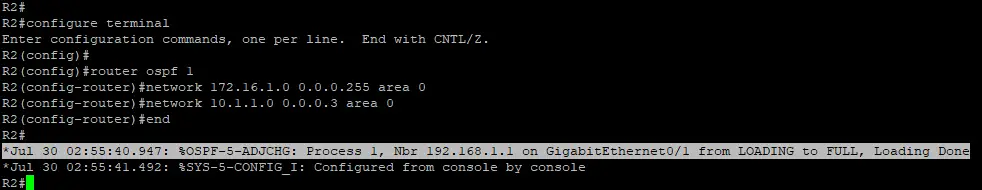
R2 CLI: under router ospf 1, network 172.16.1.0 0.0.0.255 area 0 and network 10.1.1.0 0.0.0.3 area 0 are configured, then a syslog message shows OSPF neighbor 192.168.1.1 on GigabitEthernet0/1 changing from LOADING to FULL, Loading Done.
Configuring OSPF on R2
Achievable
 

After you enter the network statements on both routers, they exchange Hellos on the shared link and go through the OSPF neighbor adjacency process (see Chapter 3.7 OSPF neighbor adjacencies).

You’ll see a console message indicating the neighbor state changed from “LOADING to FULL”. That indicates the adjacency is up.

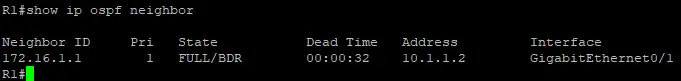
To view established adjacencies, use this command in Privileged EXEC mode:

show ip ospf neighbor

R1 CLI output for show ip ospf neighbor: Neighbor ID 172.16.1.1, Pri 1, State FULL/BDR, Dead Time 00:00:32, Address 10.1.1.2, Interface GigabitEthernet0/1.
show ip ospf neighbor output on R1
Achievable
 

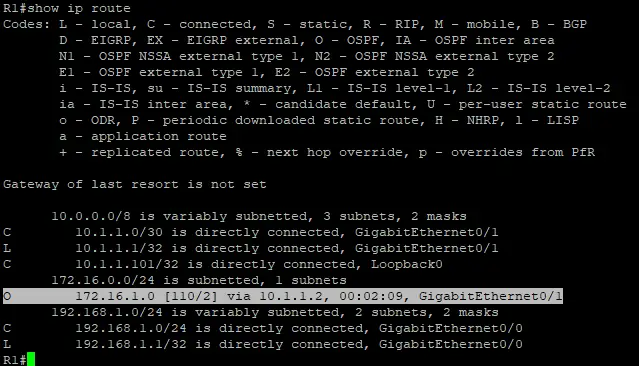
Now check whether R1 learned any OSPF routes:

R1's show ip route output lists connected and local routes for 10.1.1.0/30, 10.1.1.1/32, 10.1.1.101/32, 192.168.1.0/24 and 192.168.1.1/32, plus an OSPF route O 172.16.1.0/24 [110/2] via 10.1.1.2, GigabitEthernet0/1.
show ip route output on R1
Achievable
 

R1 has learned the route to the 172.16.1.0/24 network from R2.

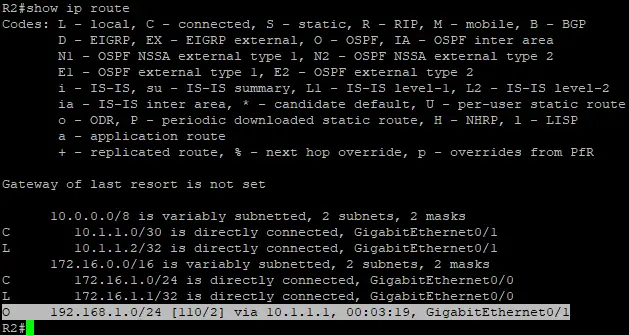
On R2, you should see the 192.168.1.0/24 network learned from R1:

R2 show ip route output with code legend: connected routes 10.1.1.0/30 and 172.16.1.0/24 on Gig0/1 and Gig0/0, and an OSPF route O 192.168.1.0/24 [110/2] via 10.1.1.1, learned through Gig0/1.
show ip route output on R2
Achievable
 

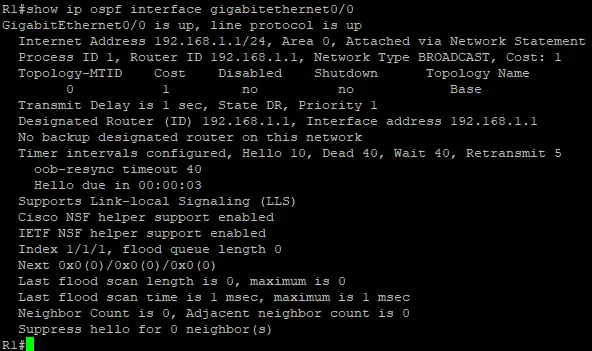
To view how a router interface is configured for OSPF, use:

show ip ospf interface

R1 CLI output of show ip ospf interface gigabitethernet0/0: address 192.168.1.1/24, area 0, process ID 1, router ID 192.168.1.1, network type BROADCAST, cost 1, state DR, priority 1, hello/dead timers 10/40, neighbor count 0.
show ip ospf interface output on R1
Achievable
 

This command shows details such as:

  • The IP address of the interface running OSPF
  • The area the interface is in
  • The OSPF Process ID
  • The Router-ID
  • The adjacency type (Network Type - BROADCAST vs. POINT-TO-POINT)
  • The interface cost
  • The interface priority (default is 1)
  • Which router is the DR and which is the BDR
  • The Hello and Dead timers

Which method did R1 use to generate the Router-ID?

(spoiler)

It used the router interface with the highest IPv4 address

Which OSPF adjacency type (Network Type) is being used on the GigabitEthernet0/1 router interface on R1?

(spoiler)

BROADCAST

Who is the DR in this adjacency and why?

(spoiler)

R1, because it has a higher Router-ID

Is R1’s GigabitEthernet0/0 and GigabitEthernet0/1 router interfaces using the default OSPF Hello and Dead timers for their adjacency type?

(spoiler)

Yes, this is the default Hello and Dead timers for Broadcast adjacencies.

One final thing that you must know about forming OSPF adjacencies which is crucial to troubleshooting OSPF and also for the CCNA 200-301 v1.1 exam, is the criteria that must be met in order for two Routers to form an adjacency:

  • The link that the two Routers are using to form the adjacency must be in the same Area on both Routers.
  • The link that the two Routers are using to form the adjacency must be in the same IP network.
  • The Hello and Dead timers must match
  • The Router-ID on both Routers must be unique. In other words, they cannot be the same.

If these criteria aren’t met (or if values that must match don’t match), the OSPF adjacency between the two routers will not come up.

Also, remember that the Process ID is only locally significant therefore, you can use the same Process ID on both Routers.

Loopback interfaces

  • Logical, not physical; assigned IP addresses
  • On PCs: 127.0.0.1 for local TCP/IP stack testing
  • On routers:
    • Used for stable connectivity and Router-ID
    • Remain up as long as router is up
    • Created manually (interface loopback [#])
    • Typically assigned /32 mask (255.255.255.255)

Configuring OSPFv2

  • Enable OSPF with: router ospf [Process ID]
    • Process ID is arbitrary and locally significant
  • OSPF Router-ID selection (in order):
    • Manually configured Router-ID (router-id x.x.x.x)
    • Highest IPv4 address on loopback interfaces
    • Highest IPv4 address on any router interface
  • OSPF interface priority:
    • ip ospf priority [0-255] (higher = more likely DR)
    • 255: always DR; 0: never DR/BDR

Network statements and wildcard masks

  • network [network-address] [wildcard-mask] area [area-id]
    • Enables OSPF on matching interfaces
    • Wildcard mask = 255.255.255.255 - subnet mask
      • /24 (255.255.255.0): 0.0.0.255
      • /30 (255.255.255.252): 0.0.0.3

OSPF adjacency formation

  • Both routers must:
    • Have interfaces in the same area
    • Have interfaces in the same IP network
    • Match Hello and Dead timers
    • Have unique Router-IDs
  • Process ID does not need to match between routers

OSPF verification commands

  • show ip ospf neighbor: view OSPF neighbors/adjacencies
  • show ip route: verify learned OSPF routes
  • show ip ospf interface: view OSPF interface details (IP, area, Process ID, Router-ID, network type, cost, interface priority, DR/BDR, timers)

Sign up for free to take 10 quiz questions on this topic

Previous
Next  | 4.1.1 Access Control Lists (ACLs)
All rights reserved ©2016 - 2026 Achievable, Inc.

How to configure OSPFv2 on Cisco routers

Loopback interfaces

Before configuring OSPF, you need to understand a special type of interface called a loopback interface.

A loopback is a logical interface. It doesn’t correspond to a physical port, but it can still be assigned an IP address.

  • On end hosts (Windows, macOS, Linux), the loopback IP address is 127.0.0.1.
  • The main purpose on PCs and servers is to verify that the operating system’s TCP/IP stack is working correctly.

When you ping 127.0.0.1 or run application tests against it, the traffic stays internal to the device. You can think of it as the host “talking to itself” to confirm it can process the layers of the TCP/IP model.

Routers can also have loopback interfaces, but they’re typically used to verify connectivity between routers. The key advantage is stability:

  • A loopback interface stays up as long as the router is up.
  • A physical interface can go down if a cable is disconnected or a link fails.

So, if one physical link fails between two routers, you can often still reach the remote router’s loopback interface (as long as you have redundant links and a valid route to that loopback IP).


Unlike end hosts, routers don’t have loopback interfaces by default. You must create them, and you can create multiple loopbacks on the same router.

To create a loopback interface on a router, go to Global Configuration mode and enter:

interface loopback [loopback #]

Network administrators often use Loopback0 as the first loopback interface, but the number is arbitrary. It’s only used to identify the loopback interface.

After you create the loopback interface, it will automatically be in the up state (unlike many physical interfaces). While still in Interface Configuration mode, assign it an IP address.


For the subnet mask, you typically use 255.255.255.255 for a loopback interface. That’s a /32 host address, and it doesn’t represent an entire subnet.

If you haven’t manually configured a routing protocol Router-ID, the IP address on a loopback interface is also used by the router as the routing protocol Router-ID.

Configuring OSPFv2

Suppose we want to configure OSPF between two routers connected over a WAN, and each router has a LAN attached.

  • R1 is connected to the 192.168.1.0/24 network.
  • R2 is connected to the 172.16.1.0/24 network.
  • The link between the routers uses the 10.1.1.0/30 network.

R1 and R2 want to advertise their directly connected LANs to each other using OSPF.

First, enter Global Configuration mode and enable the OSPF process. We’ll use a Process ID of 1.

The OSPF Process ID is arbitrary and locally significant. It is not advertised to the other router.

router ospf 1

This puts you into Routing Protocol Configuration mode, and the prompt changes to:

R1(config-router)#

OSPF router-ID selection

After enabling OSPF, the router must have an OSPF Router-ID. There are three ways the Router-ID can be selected.

A Router-ID is a 32-bit value written in dotted-decimal notation. It doesn’t have to be an IP address that actually exists on the router.

You can manually configure the OSPF Router-ID under the router ospf configuration mode using:

router-id x.x.x.x

Here, “x.x.x.x” is the Router-ID.

For example, to configure a Router-ID of “10.1.1.1” on R1:

R1(config)#configure terminal R1(config-router)#router ospf 1 R1(config-router)#router-id 10.1.1.1

However, if you don’t manually specify the Router-ID, then the router will use a Loopback interface with the highest IPv4 address out of all loopback interfaces. If no loopback interfaces exist, it will select the router interface with the highest IPv4 address out of all router interfaces.

The Router-ID selection process can be summarized like this, in order of precedence:

  1. Select the Router-ID that was manually configured (router-id [x.x.x.x]).
  2. If a Router-ID is not manually configured, then select the Loopback interface with the highest IPv4 address out of all the Loopback interfaces on the Router.
  3. If there are no Loopback interfaces on the Router, select the router interface with the highest IPv4 address out of all the router interfaces configured with IPv4 addresses.

Without the Router-ID, the OSPF process on the router cannot function.

Influencing the OSPF DR/BDR selection

In Chapter 3.7 OSPF neighbor adjacencies, we discussed that the OSPF interface priority is the first method used to determine which router becomes the DR during the DR/BDR election (part of the OSPF broadcast adjacency process).

  • The router with the highest OSPF interface priority becomes the DR.
  • The router with the second-highest interface priority becomes the BDR.

To configure the OSPF interface priority, enter Interface Configuration mode on the interface that will form the OSPF adjacency, then use:

ip ospf priority [0-255]

The OSPF Priority value ranges from 0-255. Setting the OSPF Priority value to 255 using the “ip ospf priority 255” command underneath a router interface ensures that the Router will be the DR for any OSPF adjacency that it forms on that router interface, because it’s the highest value.

Setting the OSPF Priority value to 0 using the “ip ospf priority 0” command disables the router interface from participating in a DR/BDR election, meaning, it would never become the DR or BDR for any OSPF adjacencies that it would form on that router interface.

Example: set the OSPF interface priority to 255 on GigabitEthernet0/0 so it always becomes the DR on that segment:

interface gigabitethernet0/0 ip ospf priority 255

If the OSPF priority ties between routers, the router with the highest Router-ID becomes the DR. The router with the second-highest Router-ID becomes the BDR, and it takes over as DR only if the current DR fails.

Next, we need to form the adjacency between the two routers by enabling OSPF on the router interfaces (see Chapter 3.7 OSPF neighbor adjacencies). To enable OSPF on interfaces, we configure network statements.

Network statements and wildcard masks

A network statement tells the routing protocol which router interfaces should participate in the routing process.

Here’s what happens when a router interface matches a network statement in OSPF:

  • OSPF is enabled on that interface.
  • The router starts sending OSPF Hellos out that interface.
  • The router creates LSAs for the directly connected network on that interface.
  • After an adjacency forms, those LSAs can be advertised to the OSPF neighbor.

OSPF network statements are structured like this:

Command Network of the router interface Wildcard Mask OSPF Area ID


To configure a network statement, you also need to understand the wildcard mask.

We will discuss wildcard masks in more detail in a later chapter.

A wildcard mask is the inverse of a subnet mask. It defines the range of IP addresses that an interface can fall within to match the network statement.

To derive a wildcard mask from a subnet mask, subtract the subnet mask from 255.255.255.255.

Example #1: wildcard mask for subnet mask 255.255.255.0 (/24):

255.255.255.255

0.0.0.255−255.255.255.0​

The wildcard mask is 0.0.0.255.


Example #2: wildcard mask for subnet mask 255.255.255.252 (/30):


The wildcard mask is 0.0.0.3.

Now we can enable OSPF on the two router interfaces on R1 by entering these commands under OSPF Routing Protocol Configuration mode:

Command Network of the router interface Wildcard Mask OSPF Area ID
network 192.168.1.0 0.0.0.255 area 0
network 10.1.1.0 0.0.0.3 area 0

That is:

router ospf 1 network 192.168.1.0 0.0.0.255 area 0 network 10.1.1.0 0.0.0.3 area 0 end

We must also do the same thing on R2:

Command Network of the router interface Wildcard Mask OSPF Area ID
network 172.16.1.0 0.0.0.255 area 0
network 10.1.1.0 0.0.0.3 area 0


After you enter the network statements on both routers, they exchange Hellos on the shared link and go through the OSPF neighbor adjacency process (see Chapter 3.7 OSPF neighbor adjacencies).

You’ll see a console message indicating the neighbor state changed from “LOADING to FULL”. That indicates the adjacency is up.

To view established adjacencies, use this command in Privileged EXEC mode:

show ip ospf neighbor


Now check whether R1 learned any OSPF routes:


R1 has learned the route to the 172.16.1.0/24 network from R2.

On R2, you should see the 192.168.1.0/24 network learned from R1:


To view how a router interface is configured for OSPF, use:

show ip ospf interface


This command shows details such as:

  • The IP address of the interface running OSPF
  • The area the interface is in
  • The OSPF Process ID
  • The Router-ID
  • The adjacency type (Network Type - BROADCAST vs. POINT-TO-POINT)
  • The interface cost
  • The interface priority (default is 1)
  • Which router is the DR and which is the BDR
  • The Hello and Dead timers

Which method did R1 use to generate the Router-ID?

(spoiler)

It used the router interface with the highest IPv4 address

Which OSPF adjacency type (Network Type) is being used on the GigabitEthernet0/1 router interface on R1?

(spoiler)

BROADCAST

Who is the DR in this adjacency and why?

(spoiler)

R1, because it has a higher Router-ID

Is R1’s GigabitEthernet0/0 and GigabitEthernet0/1 router interfaces using the default OSPF Hello and Dead timers for their adjacency type?

(spoiler)

Yes, this is the default Hello and Dead timers for Broadcast adjacencies.

One final thing that you must know about forming OSPF adjacencies which is crucial to troubleshooting OSPF and also for the CCNA 200-301 v1.1 exam, is the criteria that must be met in order for two Routers to form an adjacency:

  • The link that the two Routers are using to form the adjacency must be in the same Area on both Routers.
  • The link that the two Routers are using to form the adjacency must be in the same IP network.
  • The Hello and Dead timers must match
  • The Router-ID on both Routers must be unique. In other words, they cannot be the same.

If these criteria aren’t met (or if values that must match don’t match), the OSPF adjacency between the two routers will not come up.

Also, remember that the Process ID is only locally significant therefore, you can use the same Process ID on both Routers.

Key points

Loopback interfaces

  • Logical, not physical; assigned IP addresses
  • On PCs: 127.0.0.1 for local TCP/IP stack testing
  • On routers:
    • Used for stable connectivity and Router-ID
    • Remain up as long as router is up
    • Created manually (interface loopback [#])
    • Typically assigned /32 mask (255.255.255.255)

Configuring OSPFv2

  • Enable OSPF with: router ospf [Process ID]
    • Process ID is arbitrary and locally significant
  • OSPF Router-ID selection (in order):
    • Manually configured Router-ID (router-id x.x.x.x)
    • Highest IPv4 address on loopback interfaces
    • Highest IPv4 address on any router interface
  • OSPF interface priority:
    • ip ospf priority [0-255] (higher = more likely DR)
    • 255: always DR; 0: never DR/BDR

Network statements and wildcard masks

  • network [network-address] [wildcard-mask] area [area-id]
    • Enables OSPF on matching interfaces
    • Wildcard mask = 255.255.255.255 - subnet mask
      • /24 (255.255.255.0): 0.0.0.255
      • /30 (255.255.255.252): 0.0.0.3

OSPF adjacency formation

  • Both routers must:
    • Have interfaces in the same area
    • Have interfaces in the same IP network
    • Match Hello and Dead timers
    • Have unique Router-IDs
  • Process ID does not need to match between routers

OSPF verification commands

  • show ip ospf neighbor: view OSPF neighbors/adjacencies
  • show ip route: verify learned OSPF routes
  • show ip ospf interface: view OSPF interface details (IP, area, Process ID, Router-ID, network type, cost, interface priority, DR/BDR, timers)

More from Configuring Cisco Routers

  • Initial router configuration and static routes