


This browser is too old to run Achievable.

Update it, or open this page in a current version of Chrome, Safari, Firefox or Edge. On an iPhone or iPad, update iOS: every browser there runs on the version of Safari that comes with it.

Achievable logoAchievable logo
CMA Part 1
Sign in
Sign up
Purchase
Textbook
Practice exams
Support
How it works
Resources
Exam catalog
Mountain with a flag at the peak
Textbook
Introduction
1. External financial reporting decisions
2. Planning, budgeting, and forecasting
3. Performance management
4. Cost management
5. Internal control
5.1 Governance, risk and compliance
5.1.1 Internal control objectives and the COSO Framework
5.1.2 Responsibility for internal control and segregation of duties
5.1.3 Internal control limitations, risks, and deficiencies
5.1.4 Corporate governance structure and responsibilities
5.1.5 Corporate governance roles and responsibilities
5.1.6 External audit
5.1.7 The Sarbanes-oxley Act
5.1.8 Other regulatory bodies
5.2 System controls and security measures
6. Technology and analytics
Wrapping up
Achievable logoAchievable logo
5.1.2 Responsibility for internal control and segregation of duties
Achievable CMA Part 1
5. Internal control
5.1. Governance, risk and compliance
Our CMA Part 1 course is currently in development and is a work-in-progress.

Responsibility for internal control and segregation of duties

5 min read
Font
Discuss
Share
Feedback

Who is responsible for internal control?

Responsibility for internal control is distributed across various levels of an organization, with specific roles assigned to individuals and groups within the entity, as well as external parties such as regulators and auditors. A sound internal control system relies on the collaboration of all these players to be effective.

Party Primary responsibility Key point
Board of directors and audit committee Oversees the internal control system and sets the tone at the top Reviews internal and external audit reports to monitor the control framework
Senior management (e.g., CEO, CFO) Designs, implements, and maintains internal controls Sets control policy, allocates resources, and reinforces an ethical culture
Operational and functional managers Applies and monitors controls within their own areas Acts as the first line of defense and reports control issues to senior management
Internal audit function Independently assesses whether controls are designed and operating effectively Reports to the audit committee or board, not to management, to preserve independence
Employees Comply with control policies and procedures in daily work Report irregularities, control weaknesses, or unethical behavior
External auditors Consider internal control when planning every audit For public companies subject to SOX Section 404(b), external auditors also evaluate and report on the effectiveness of internal control over financial reporting; they don’t design or implement controls
Regulators and standard-setting bodies Establish laws and frameworks that shape internal control practice For example, the Sarbanes-Oxley Act (SOX) mandates internal control over financial reporting requirements in the US

Personnel policies and the control environment

An effective control environment begins with strong personnel policies and procedures. These policies guide the recruitment, training, supervision, and evaluation of employees, ensuring that competent and trustworthy individuals are placed in positions of responsibility. Clearly defined job descriptions, ethical codes of conduct, and ongoing professional development support a culture of accountability and transparency, which are critical for internal control effectiveness.

Segregation of duties

Definitions
Segregation of duties
An internal control principle that requires dividing four key responsibilities among different individuals: authorizing transactions, recording transactions, maintaining custody of related assets, and periodically reconciling assets to records. By separating these functions, organizations reduce the risk of error, misuse, or fraud and strengthen the system of checks and balances.

Key functional responsibilities to segregate

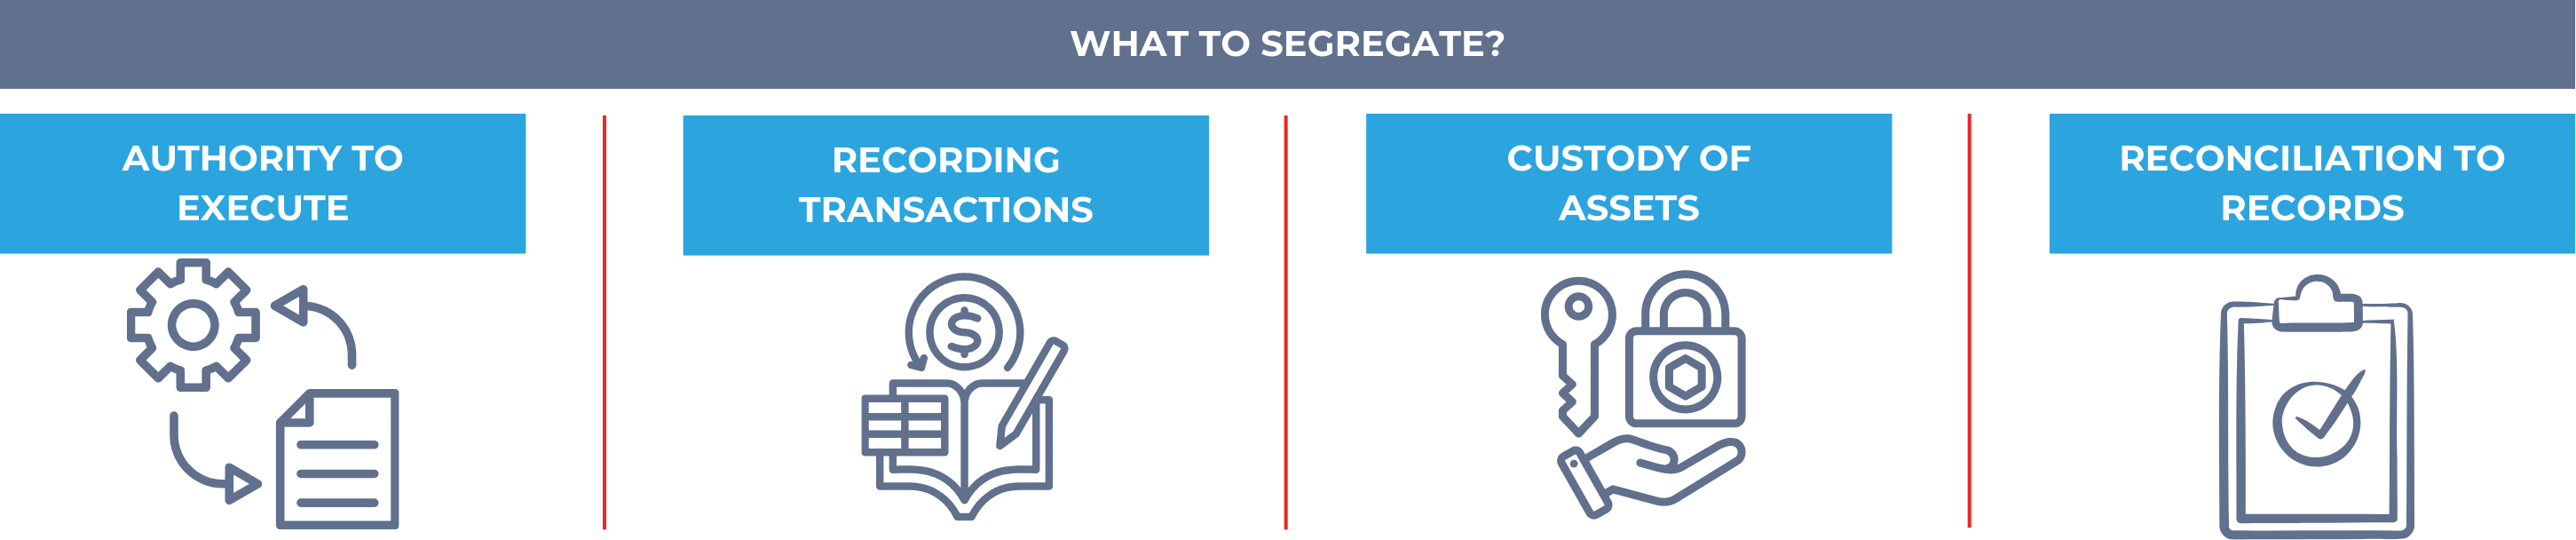
Internal control best practices recommend that the following four types of responsibilities be segregated to different people or departments:

Segregation of accounting duties
Achievable
  1. Authority to execute transactions - This refers to the approval or initiation of transactions. For example, a purchasing manager may have the authority to place orders for goods and services.
  2. Recording transactions - This involves maintaining the accounting records, such as entering transactions into the general ledger or subledgers. A separate accounting staff member would typically perform this function.
  3. Custody of assets - This responsibility includes physical possession or control over assets such as cash, inventory, or fixed assets. For instance, a warehouse supervisor may manage inventory storage and access.
  4. Reconciliation of assets to records - Periodic reconciliation ensures that physical assets match the recorded balances in the accounting system. Ideally, someone who does not have access to assets or records them should perform this task to maintain objectivity.

Failure to segregate these duties increases the risk that errors or fraud could occur and go undetected. For example, if one person is responsible for authorizing payments, recording them, and reconciling bank statements, they could easily conceal unauthorized transactions.

Examples of segregation of duties by department

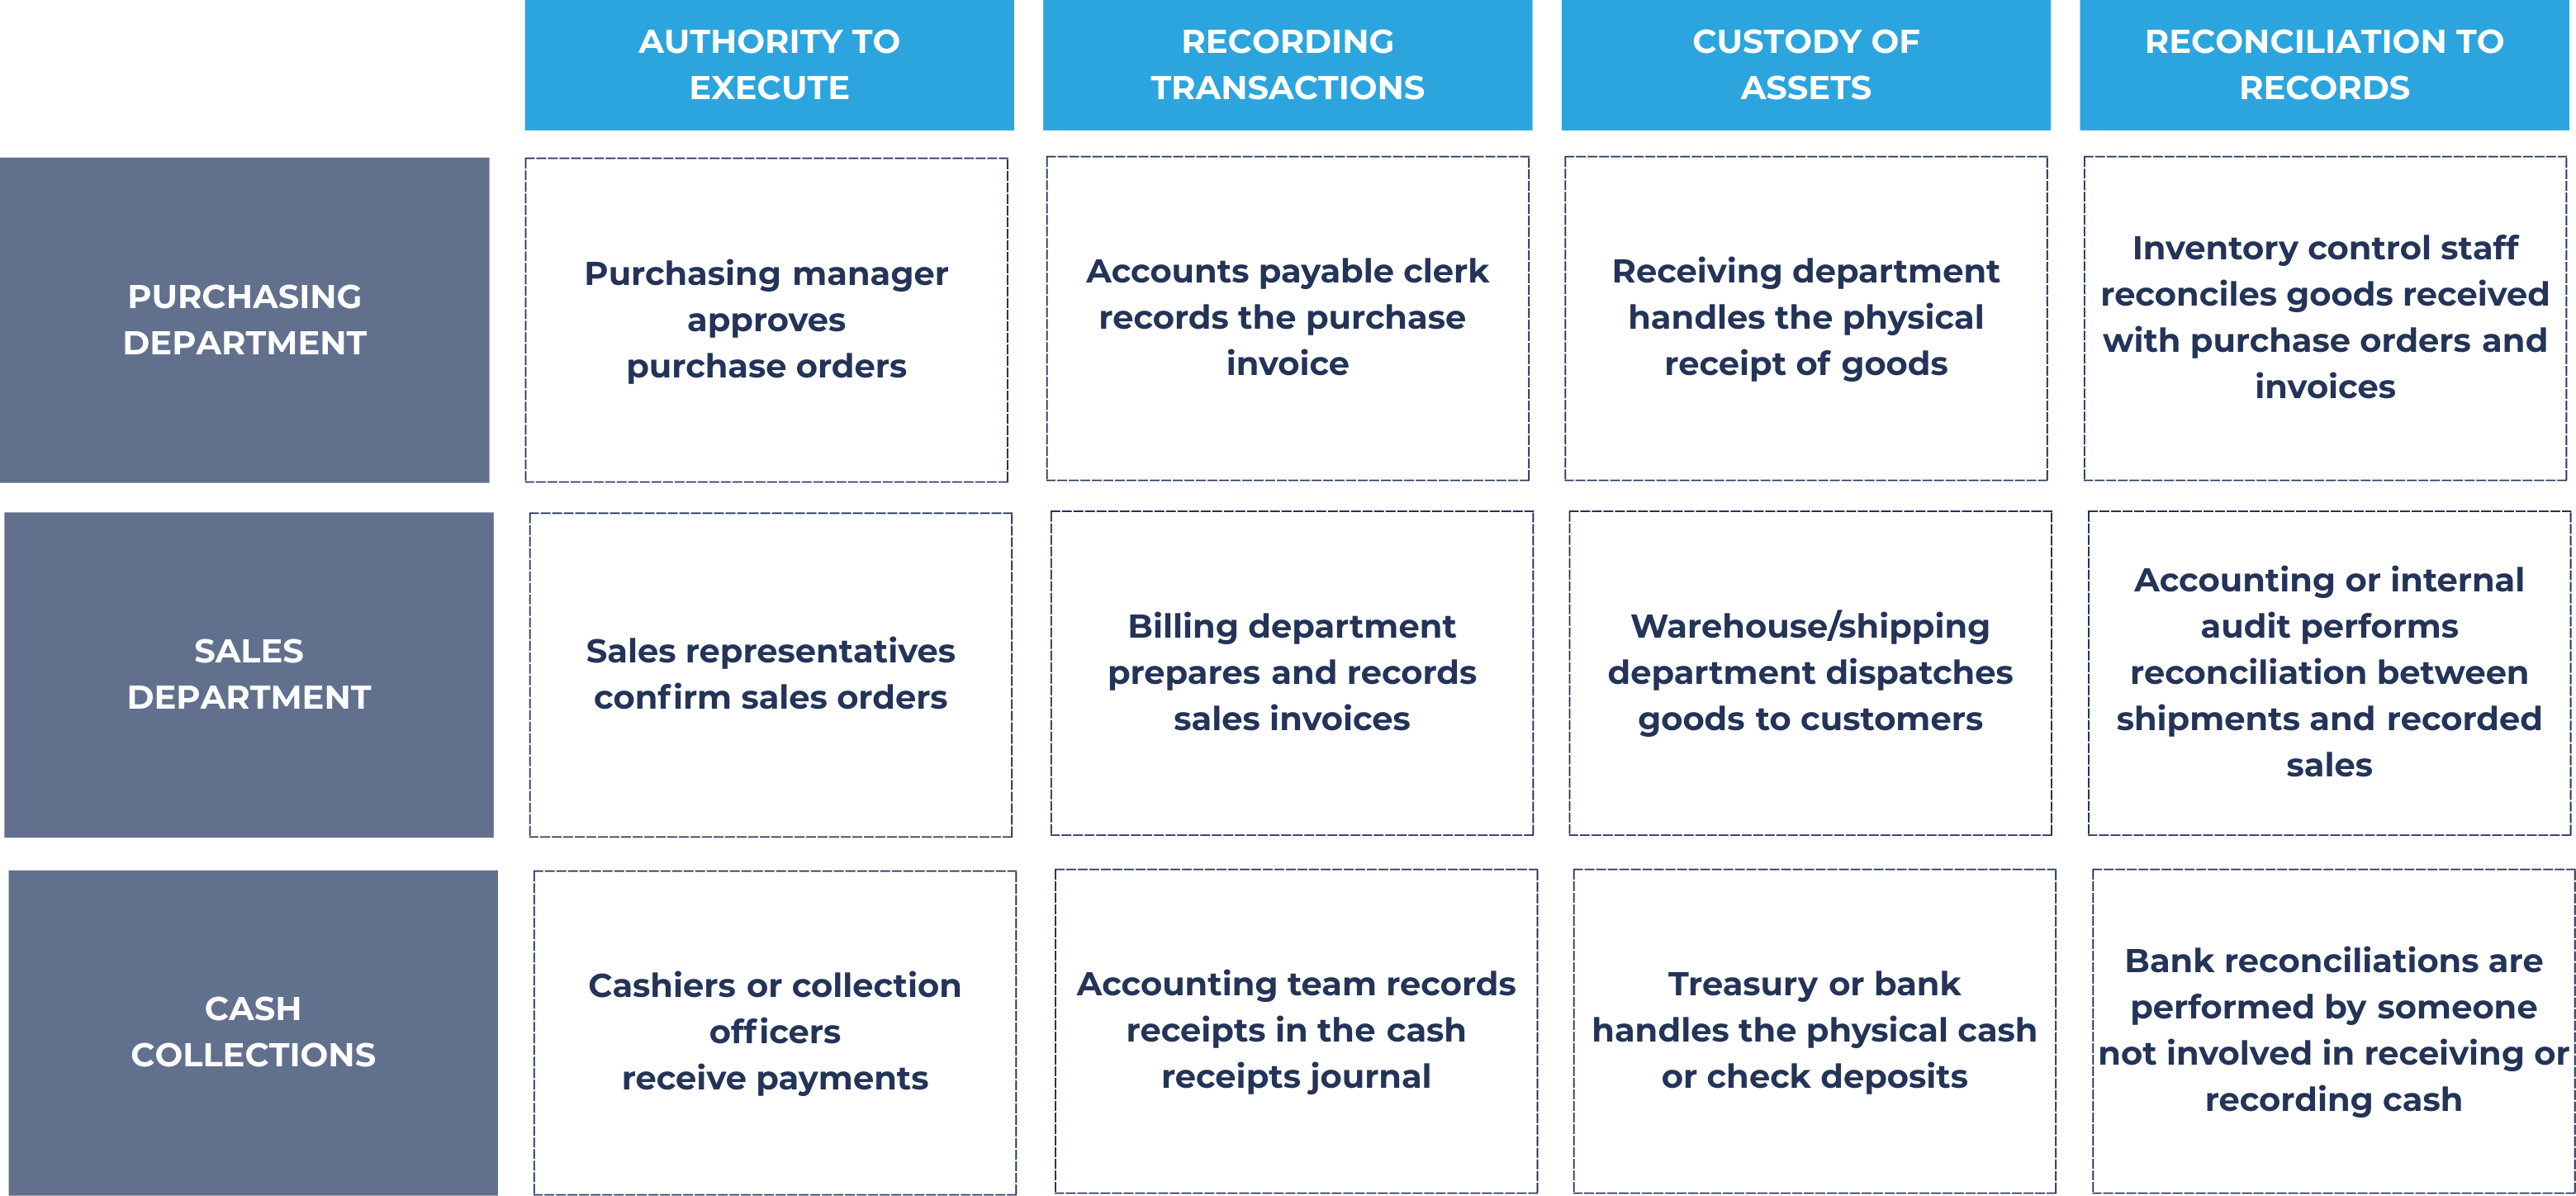
To illustrate how segregation of duties can be applied in practice, consider the following departmental examples:

Examples of segregation of accounting duties
Achievable

Example: Cash receipts

A company separates cash receipts duties across four people: the mailroom clerk opens incoming mail and lists the checks received (custody), the cashier deposits the checks (custody), accounts receivable posts the payments to customer accounts (recording), and an employee independent of all three performs the bank reconciliation (reconciliation). If the accounts receivable clerk also handled incoming cash, they could pocket a customer’s payment and cover the shortage by crediting it against a later customer’s payment - a fraud scheme known as lapping.

Segregation of duties can be defeated when two or more employees collude, or when management overrides the controls in place; these inherent limitations are covered in the next chapter, Internal control limitations, risks, and deficiencies.

Responsibility for internal control

  • Shared across organization: board/audit committee sets tone and oversees; senior management designs/implements controls; operational managers apply/monitor as first line of defense
  • Internal audit independently assesses control effectiveness, reports to audit committee/board (not management) for independence
  • Employees comply with policies and report issues; external auditors consider controls when planning audits (and under SOX 404(b), evaluate/report on ICFR for public companies) but don’t design controls
  • Regulators (e.g., SOX) establish laws shaping control requirements

Personnel policies and control environment

  • Strong control environment starts with hiring, training, supervision, and evaluation policies
  • Clear job descriptions, codes of conduct, and professional development build accountability culture

Segregation of duties

  • Core principle: divide four key responsibilities among different people to reduce error/fraud risk
    • Authorization (approving transactions)
    • Recording (bookkeeping/ledger entries)
    • Custody (physical control of assets)
    • Reconciliation (comparing records to actual assets, ideally by independent party)
  • Failure to segregate allows one person to commit and conceal fraud (e.g., authorizing, recording, and reconciling same transaction)

Application example: cash receipts

  • Typical segregation: mailroom opens mail/lists checks (custody), cashier deposits (custody), AR posts payments (recording), independent employee reconciles bank statement (reconciliation)
  • Combining duties enables schemes like lapping (misusing one customer’s payment to cover theft from another)
  • Segregation can still fail via collusion or management override (covered in next chapter)

Sign up for free to take 8 quiz questions on this topic

Previous
Next  | 5.1.3 Internal control limitations, risks, and deficiencies
All rights reserved ©2016 - 2026 Achievable, Inc.

Responsibility for internal control and segregation of duties

Who is responsible for internal control?

Responsibility for internal control is distributed across various levels of an organization, with specific roles assigned to individuals and groups within the entity, as well as external parties such as regulators and auditors. A sound internal control system relies on the collaboration of all these players to be effective.

Party Primary responsibility Key point
Board of directors and audit committee Oversees the internal control system and sets the tone at the top Reviews internal and external audit reports to monitor the control framework
Senior management (e.g., CEO, CFO) Designs, implements, and maintains internal controls Sets control policy, allocates resources, and reinforces an ethical culture
Operational and functional managers Applies and monitors controls within their own areas Acts as the first line of defense and reports control issues to senior management
Internal audit function Independently assesses whether controls are designed and operating effectively Reports to the audit committee or board, not to management, to preserve independence
Employees Comply with control policies and procedures in daily work Report irregularities, control weaknesses, or unethical behavior
External auditors Consider internal control when planning every audit For public companies subject to SOX Section 404(b), external auditors also evaluate and report on the effectiveness of internal control over financial reporting; they don’t design or implement controls
Regulators and standard-setting bodies Establish laws and frameworks that shape internal control practice For example, the Sarbanes-Oxley Act (SOX) mandates internal control over financial reporting requirements in the US

Personnel policies and the control environment

An effective control environment begins with strong personnel policies and procedures. These policies guide the recruitment, training, supervision, and evaluation of employees, ensuring that competent and trustworthy individuals are placed in positions of responsibility. Clearly defined job descriptions, ethical codes of conduct, and ongoing professional development support a culture of accountability and transparency, which are critical for internal control effectiveness.

Segregation of duties

Definitions
Segregation of duties
An internal control principle that requires dividing four key responsibilities among different individuals: authorizing transactions, recording transactions, maintaining custody of related assets, and periodically reconciling assets to records. By separating these functions, organizations reduce the risk of error, misuse, or fraud and strengthen the system of checks and balances.

Key functional responsibilities to segregate

Internal control best practices recommend that the following four types of responsibilities be segregated to different people or departments:

  1. Authority to execute transactions - This refers to the approval or initiation of transactions. For example, a purchasing manager may have the authority to place orders for goods and services.
  2. Recording transactions - This involves maintaining the accounting records, such as entering transactions into the general ledger or subledgers. A separate accounting staff member would typically perform this function.
  3. Custody of assets - This responsibility includes physical possession or control over assets such as cash, inventory, or fixed assets. For instance, a warehouse supervisor may manage inventory storage and access.
  4. Reconciliation of assets to records - Periodic reconciliation ensures that physical assets match the recorded balances in the accounting system. Ideally, someone who does not have access to assets or records them should perform this task to maintain objectivity.

Failure to segregate these duties increases the risk that errors or fraud could occur and go undetected. For example, if one person is responsible for authorizing payments, recording them, and reconciling bank statements, they could easily conceal unauthorized transactions.

Examples of segregation of duties by department

To illustrate how segregation of duties can be applied in practice, consider the following departmental examples:

Example: Cash receipts

A company separates cash receipts duties across four people: the mailroom clerk opens incoming mail and lists the checks received (custody), the cashier deposits the checks (custody), accounts receivable posts the payments to customer accounts (recording), and an employee independent of all three performs the bank reconciliation (reconciliation). If the accounts receivable clerk also handled incoming cash, they could pocket a customer’s payment and cover the shortage by crediting it against a later customer’s payment - a fraud scheme known as lapping.

Segregation of duties can be defeated when two or more employees collude, or when management overrides the controls in place; these inherent limitations are covered in the next chapter, Internal control limitations, risks, and deficiencies.

Key points

Responsibility for internal control

  • Shared across organization: board/audit committee sets tone and oversees; senior management designs/implements controls; operational managers apply/monitor as first line of defense
  • Internal audit independently assesses control effectiveness, reports to audit committee/board (not management) for independence
  • Employees comply with policies and report issues; external auditors consider controls when planning audits (and under SOX 404(b), evaluate/report on ICFR for public companies) but don’t design controls
  • Regulators (e.g., SOX) establish laws shaping control requirements

Personnel policies and control environment

  • Strong control environment starts with hiring, training, supervision, and evaluation policies
  • Clear job descriptions, codes of conduct, and professional development build accountability culture

Segregation of duties

  • Core principle: divide four key responsibilities among different people to reduce error/fraud risk
    • Authorization (approving transactions)
    • Recording (bookkeeping/ledger entries)
    • Custody (physical control of assets)
    • Reconciliation (comparing records to actual assets, ideally by independent party)
  • Failure to segregate allows one person to commit and conceal fraud (e.g., authorizing, recording, and reconciling same transaction)

Application example: cash receipts

  • Typical segregation: mailroom opens mail/lists checks (custody), cashier deposits (custody), AR posts payments (recording), independent employee reconciles bank statement (reconciliation)
  • Combining duties enables schemes like lapping (misusing one customer’s payment to cover theft from another)
  • Segregation can still fail via collusion or management override (covered in next chapter)

More from Governance, risk and compliance

  • Internal control objectives and the COSO Framework
  • Internal control limitations, risks, and deficiencies
  • Corporate governance structure and responsibilities
  • Corporate governance roles and responsibilities
  • External audit