


This browser is too old to run Achievable.

Update it, or open this page in a current version of Chrome, Safari, Firefox or Edge. On an iPhone or iPad, update iOS: every browser there runs on the version of Safari that comes with it.

Achievable logoAchievable logo
CCNA
Sign in
Sign up
Purchase
Textbook
Practice exams
Support
How it works
Resources
Exam catalog
Mountain with a flag at the peak
Textbook
Introduction
1. Introduction to networking
2. Administering Ethernet LANs
2.1 Wired network access
2.2 Hosts communicating on a Local Area Network
2.3 Virtual LANs (VLANs)
2.4 Layer 2 link redundancy
2.5 Configuring Cisco Switches
2.5.1 Introduction to Cisco's Internetworking Operating System (IOS)
2.5.2 MAC address table & VLAN configuration
2.5.3 The Voice VLAN and Layer 1 troubleshooting
2.5.4 How to configure Rapid PVST+ and Etherchannels
3. IP connectivity
4. Network services
5. IPv6
6. Wireless networking
7. Network management and administering network devices
8. Network security fundamentals
9. Network automation and programmability
Wrapping up
Achievable logoAchievable logo
2.5.4 How to configure Rapid PVST+ and Etherchannels
Achievable CCNA
2. Administering Ethernet LANs
2.5. Configuring Cisco Switches
Our CCNA course is currently in development and is a work-in-progress.

How to configure Rapid PVST+ and Etherchannels

21 min read
Font
Discuss
Share
Feedback

Rapid PVST+ tuning

Although Spanning Tree is enabled by default on Cisco switches, the default behavior isn’t always what you want in a real network. STP usually needs some tuning so the root bridge and forwarding paths line up with your design.

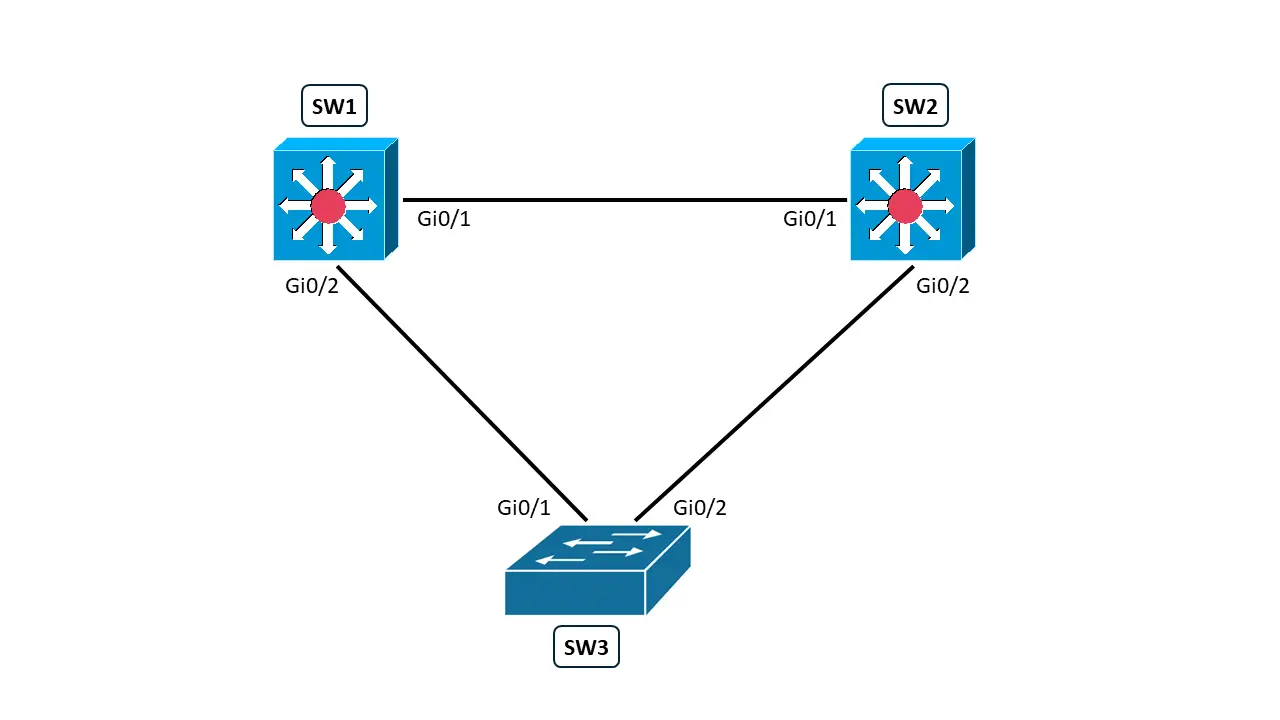
Here’s the scenario: three switches are connected to each other with trunk links - SW1, SW2, and SW3. SW1 and SW2 are distribution switches, and SW3 is the access switch.

Three switches form a triangle: SW1 Gi0/1 connects to SW2 Gi0/1, SW1 Gi0/2 connects to SW3 Gi0/1, and SW2 Gi0/2 connects to SW3 Gi0/2, creating a redundant loop between all three.
3 Switches connected to each other
Achievable
 

In this design:

  • SW1 should be the Primary Root Bridge for VLAN 2 and the Secondary (backup) Root Bridge for VLAN 3.
  • SW2 should be the Primary Root Bridge for VLAN 3 and the Secondary Root Bridge for VLAN 2.

That way, SW1 and SW2 back each other up if one fails.

This makes SW3 the Non-Root Bridge. For VLAN 2, SW3’s:

  • Root Port should be GigabitEthernet 0/1.
  • GigabitEthernet 0/2 should be an Alternate Port.

Which port on SW3 should be the Root Port for VLAN 3 traffic and which port should be the Alternate Port?

(spoiler)
  • SW3’s GigabitEthernet 0/2 should be the Root Port for VLAN 3 traffic
  • SW3’s GigabitEthernet 0/1 should be the Alternate Port for VLAN 3 traffic

If you leave all three switches at their default STP settings, they might not converge the way you intend. With the default bridge priority on all switches, the root bridge election comes down to the switch with the lowest base MAC address.

What is the default Bridge Priority value on all Switches running STP?

(spoiler)

32768

Now consider what happens if SW3 has the lowest base MAC address. SW3 could become the root bridge, which is usually not what you want in a hierarchical design.

Having an access switch as the root bridge for your LAN can create bottlenecks and suboptimal traffic paths.

To prevent that, you configure SW1 and SW2 so they reliably become the root bridges for their intended VLANs.

Verify and enable Rapid PVST+

Before tuning priorities, make sure the switches are running Rapid PVST+. Some switches may still be using the legacy STP version (802.1D / PVST+) by default.

To verify the current STP mode, use:

show spanning-tree

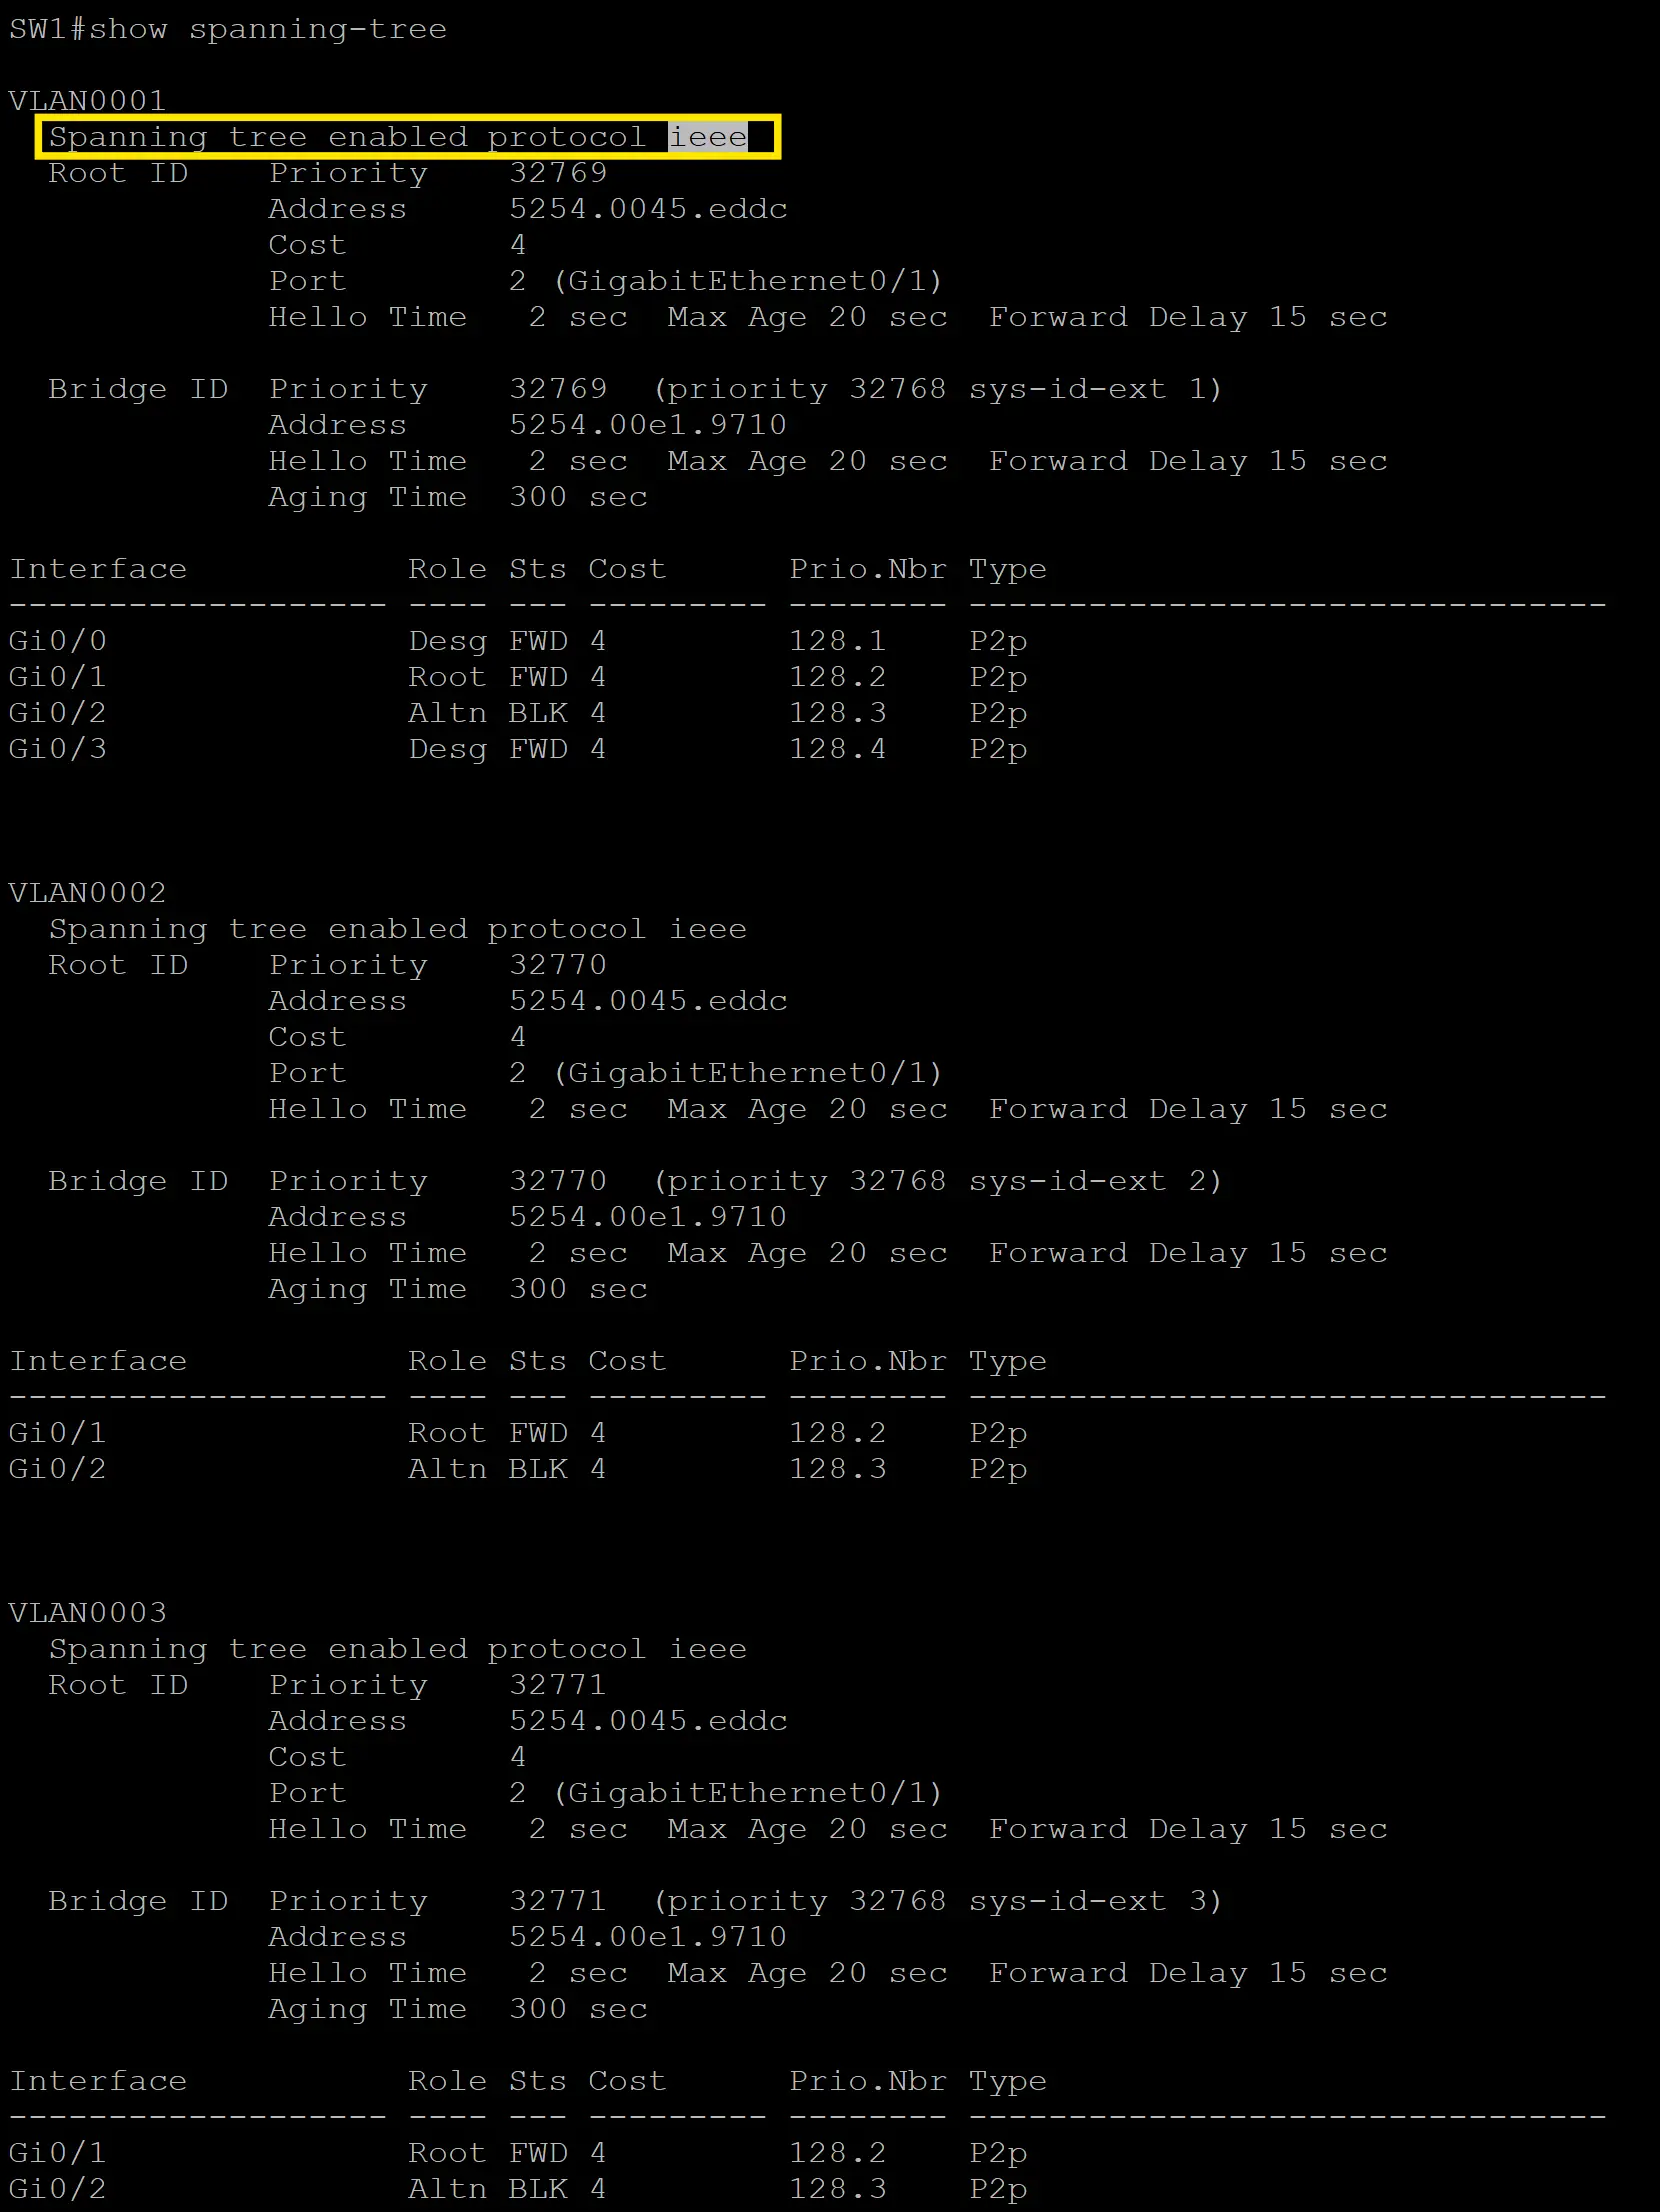
Terminal output of show spanning-tree on SW1 for VLANs 1-3, each using IEEE protocol with root bridge address 5254.0045.eddc reached via Gi0/1 (Root, FWD, cost 4). VLAN1 also shows Gi0/0 and Gi0/3 as Designated forwarding ports and Gi0/2 as Alternate blocking; VLANs 2 and 3 show Gi0/1 Root forwarding and Gi0/2 Alternate blocking.
show spanning-tree output displaying 802.1D version running
Achievable
 

This output also shows STP information per VLAN. With Cisco Per-VLAN Spanning Tree, each VLAN runs its own STP instance.

In the output, look for the line:

  • Spanning tree enabled protocol

If you see ieee, the switch is running the legacy STP mode (802.1D / PVST+). In this scenario, you want to change all three switches to Rapid PVST+.

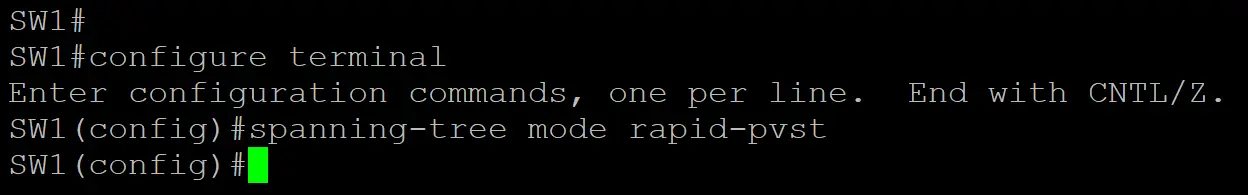
To enable Rapid PVST+, go to global configuration mode and enter:

spanning-tree mode rapid-pvst

SW1 CLI session entering global configuration mode and running the command spanning-tree mode rapid-pvst to enable Rapid PVST+.
Configuring Rapid PVST+
Achievable
 

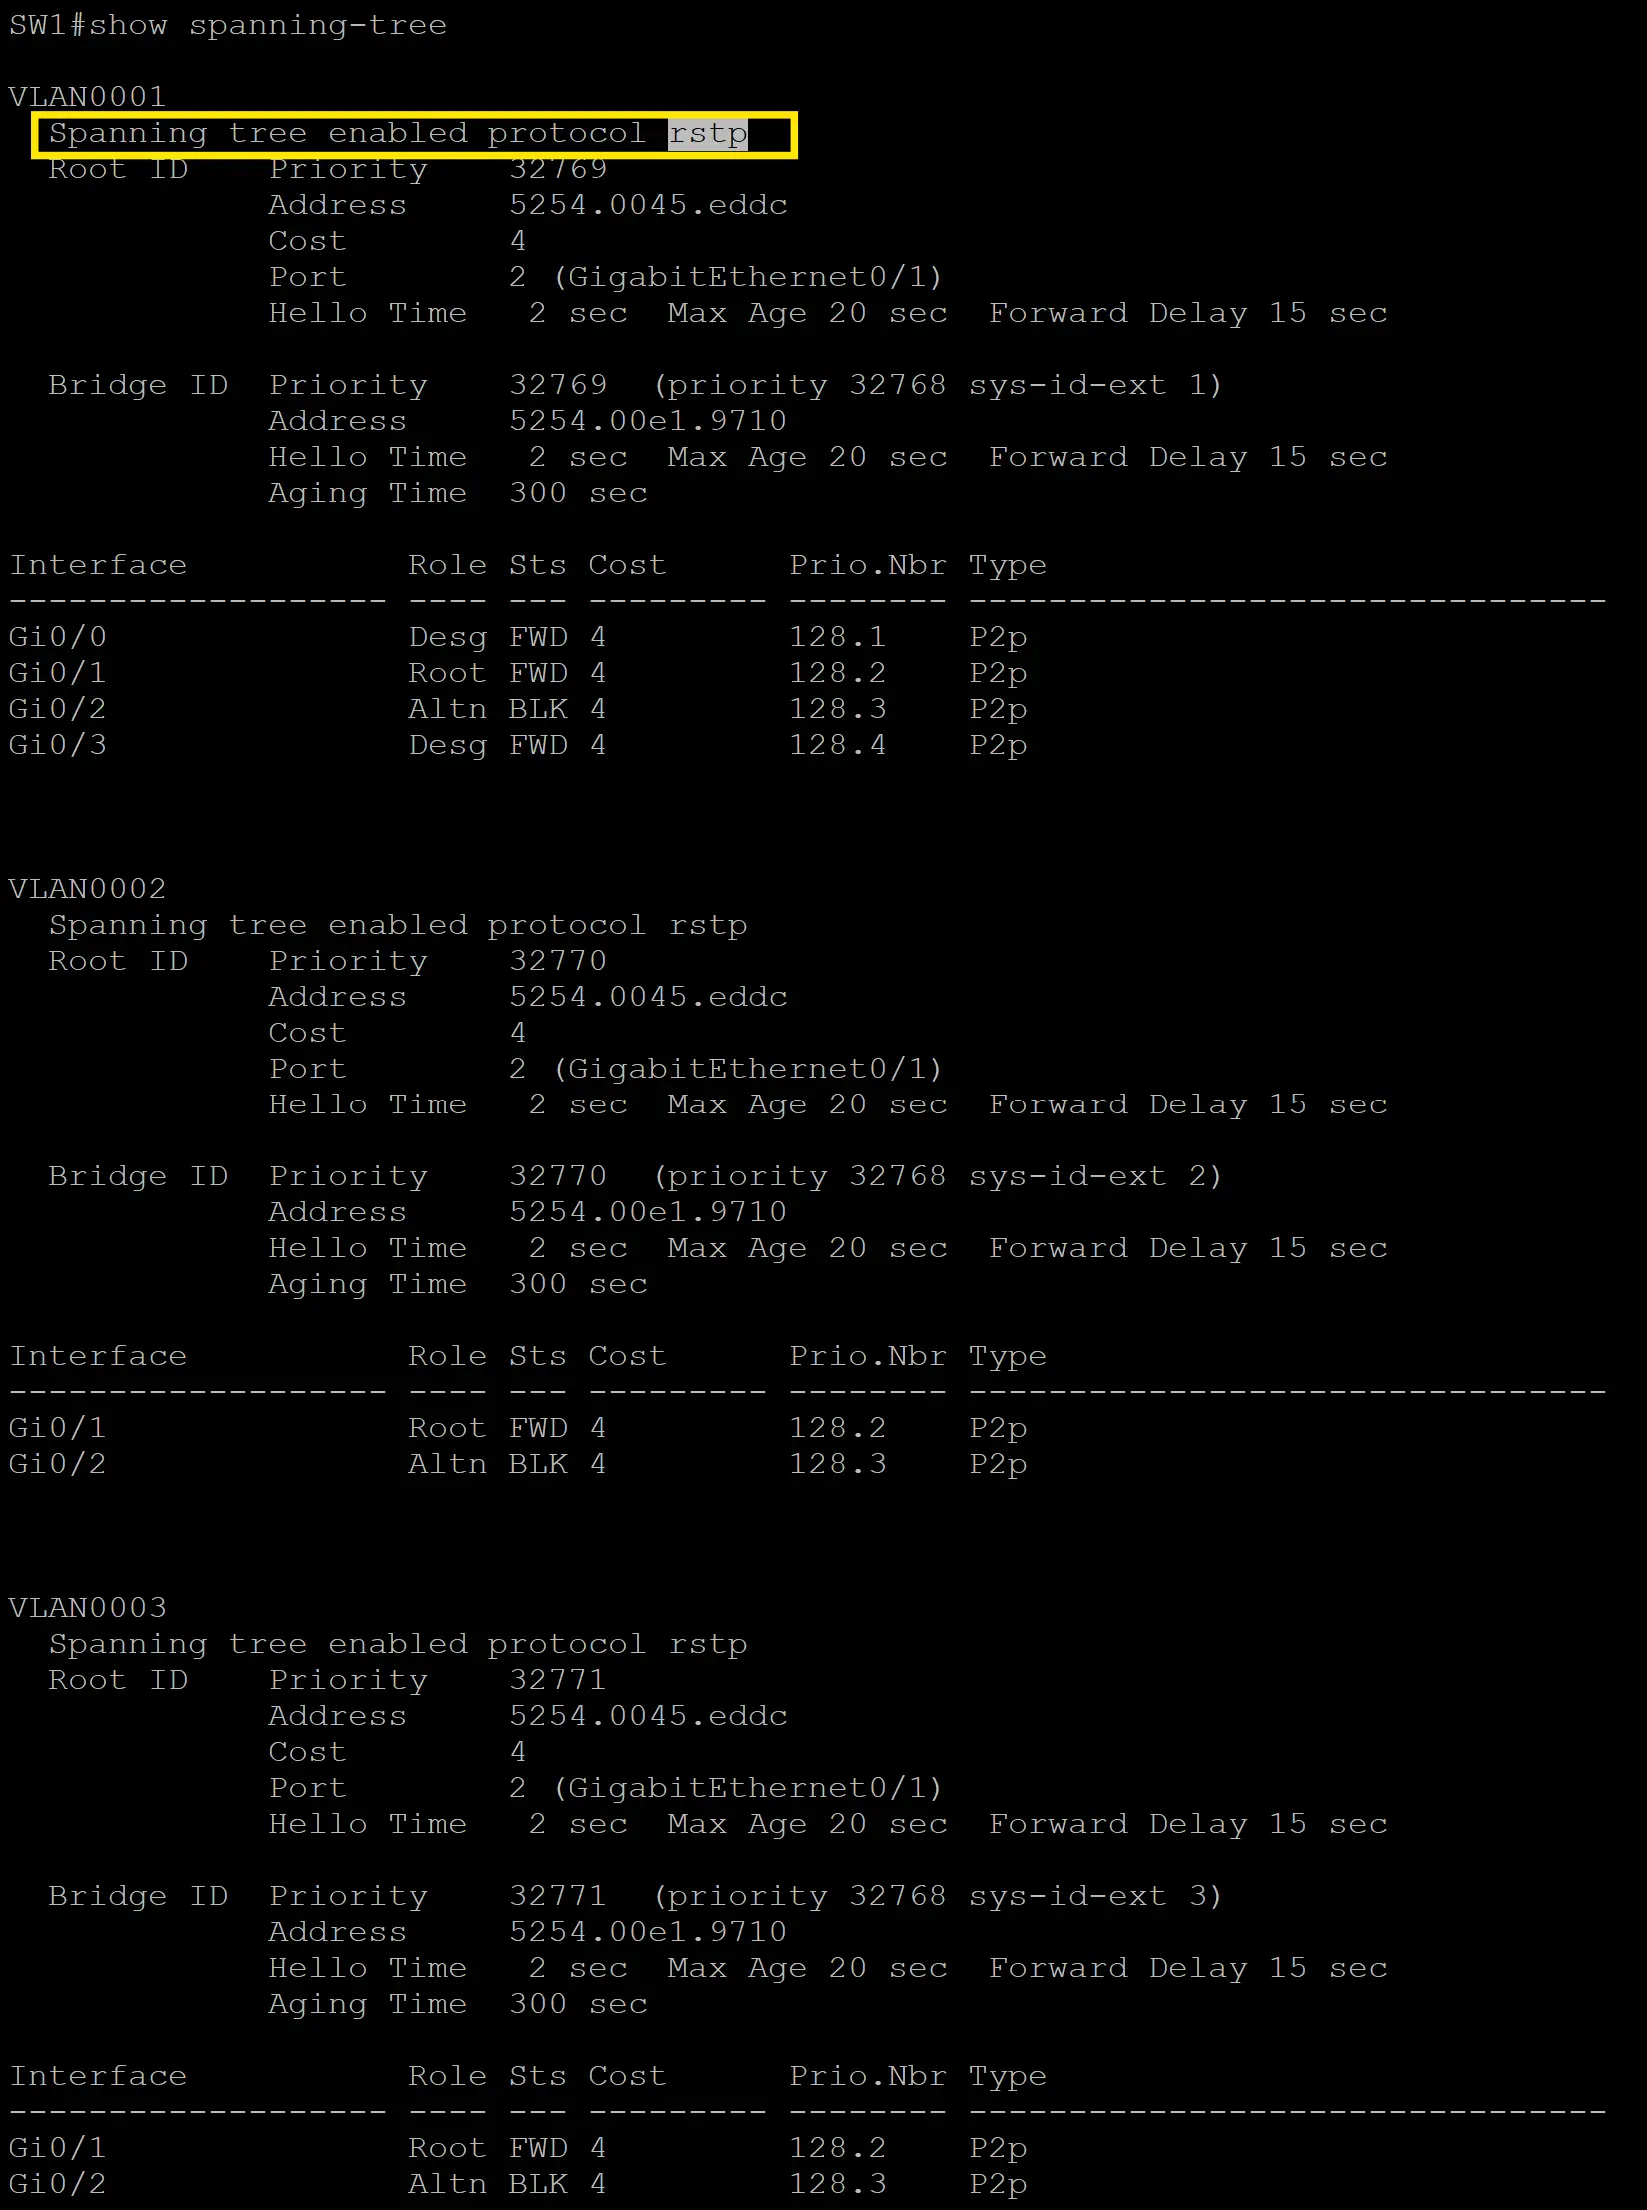
If you run show spanning-tree again, you should now see the protocol listed as rstp, which indicates Rapid PVST+.

SW1 show spanning-tree output for VLANs 1-3, each using rstp protocol with root ID address 5254.0045.eddc reached via Gi0/1. On SW1, Gi0/1 is Root FWD, Gi0/2 is Altn BLK, and for VLAN1 only, Gi0/0 and Gi0/3 are Desg FWD, all with cost 4.
show spanning-tree output displaying Rapid PVST+ version running
Achievable

This should be configured on all 3 switches.

Set root bridge priorities per VLAN

Now you can tune SW1 and SW2 so they become the intended root bridges.

  • Make SW1 the Primary Root Bridge for VLAN 2 and the Secondary Root Bridge for VLAN 3.
  • Make SW2 the Primary Root Bridge for VLAN 3 and the Secondary Root Bridge for VLAN 2.

On SW1, in global configuration mode, set:

spanning-tree vlan 2 priority 4096 spanning-tree vlan 3 priority 8192

On SW2, do the opposite:

spanning-tree vlan 2 priority 8192 spanning-tree vlan 3 priority 4096

Verify the result on SW1 and SW2

To check the VLAN 2 STP instance on SW1 and SW2, use:

  • show spanning-tree vlan 2

This filters the output so you only see the VLAN 2 STP instance.

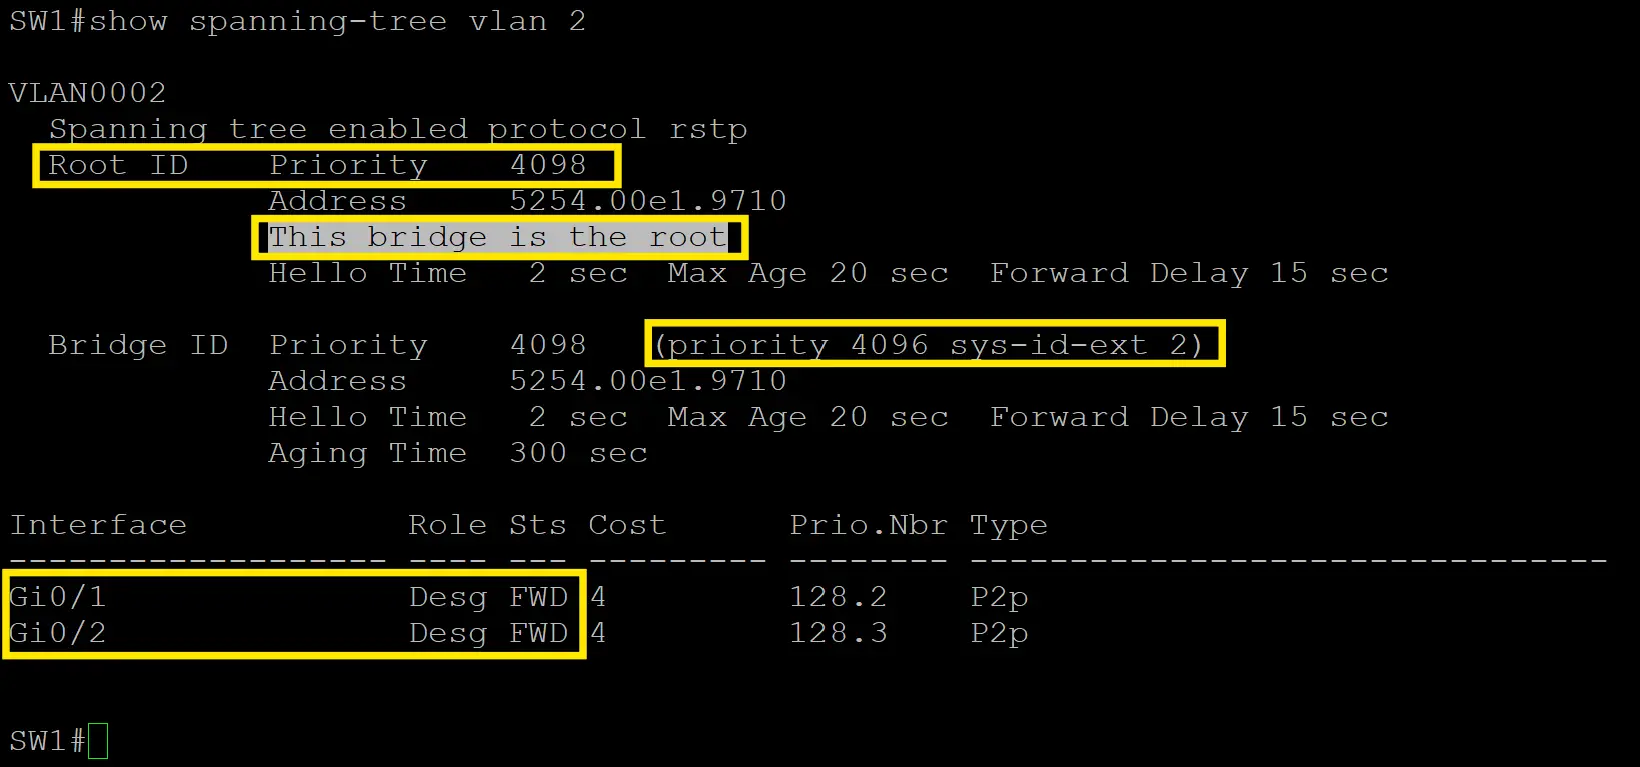
Terminal output of show spanning-tree vlan 2 on SW1: Root ID priority 4098, marked as this bridge is the root; Bridge ID priority 4098 (priority 4096 plus sys-id-ext 2); interfaces Gi0/1 and Gi0/2 both show role Desg, status FWD, cost 4, confirming SW1 is the VLAN 2 root bridge with both ports designated and forwarding.
show spanning-tree vlan 2 output on SW1
Achievable
 

In the output:

  • The Root ID section shows which switch is the root bridge for that VLAN.
  • The Bridge ID section shows the local switch’s STP identity.

On SW1, you’ll see it declare “This bridge is the root” for VLAN 2. You’ll also notice:

  • The configured priority was 4096.
  • The displayed priority becomes 4098 because the System-ID Extension adds the VLAN number (here, 4096 + 2).

Because SW1 is the root bridge for VLAN 2, its active ports for that VLAN take the Designated Port role (Desg) and are in the Forwarding state (FWD).

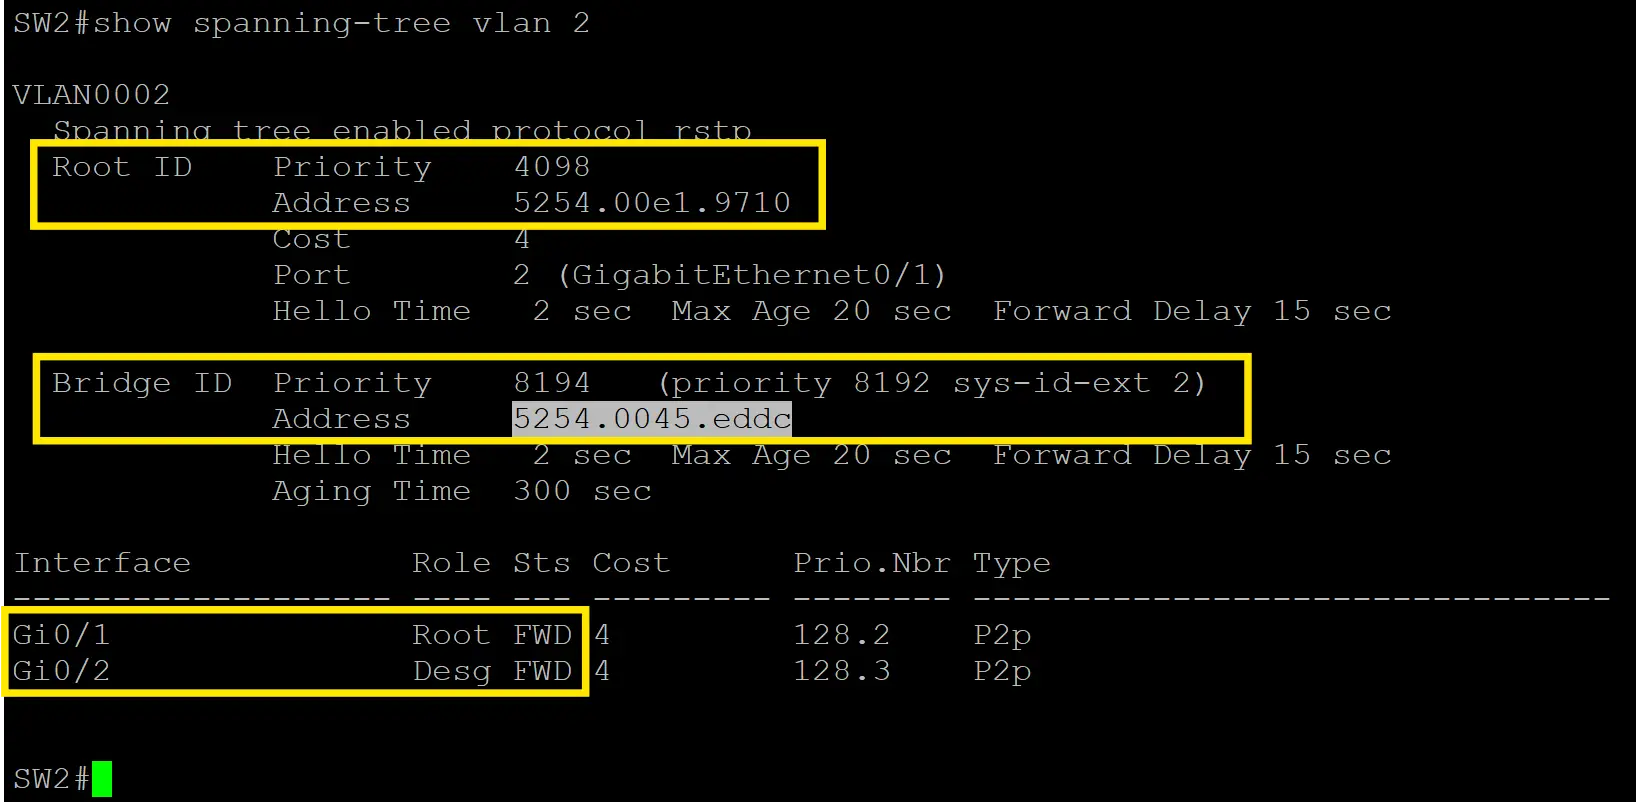
On SW2, the Root ID shows SW1’s base MAC address as the root for VLAN 2. SW2’s Bridge ID differs from the Root ID because SW2 is not the root bridge for VLAN 2.

Terminal output of show spanning-tree vlan 2 on SW2: Root ID priority 4098, address 5254.00e1.9710, cost 4 via port Gi0/1; Bridge ID priority 8194 (8192 plus sys-id-ext 2), address 5254.0045.eddc. Interface table shows Gi0/1 as Root, forwarding, cost 4; Gi0/2 as Designated, forwarding, cost 4.
show spanning-tree vlan 2 output on SW2
Achievable
 

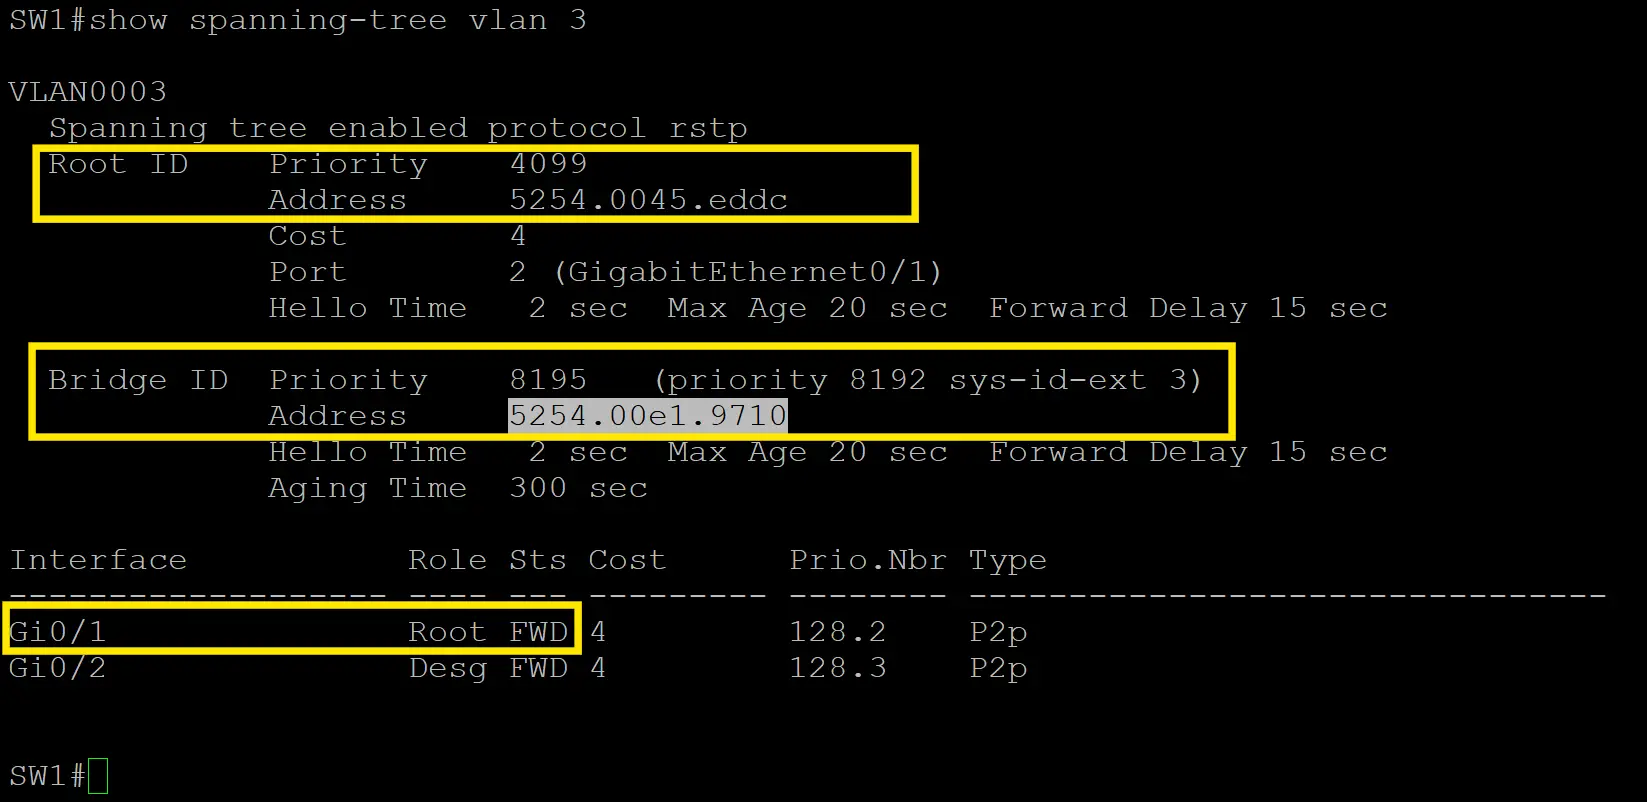
If you run the same check for VLAN 3, you should see the opposite behavior:

SW1 output for show spanning-tree vlan 3: Root ID priority 4099, address 5254.0045.eddc, cost 4 via port GigabitEthernet0/1; Bridge ID priority 8195 (8192 plus sys-id-ext 3), address 5254.00e1.9710. Interface table shows Gi0/1 as Root, forwarding, cost 4, and Gi0/2 as Designated, forwarding, cost 4.
show spanning-tree vlan 3 output on SW1
Achievable
 

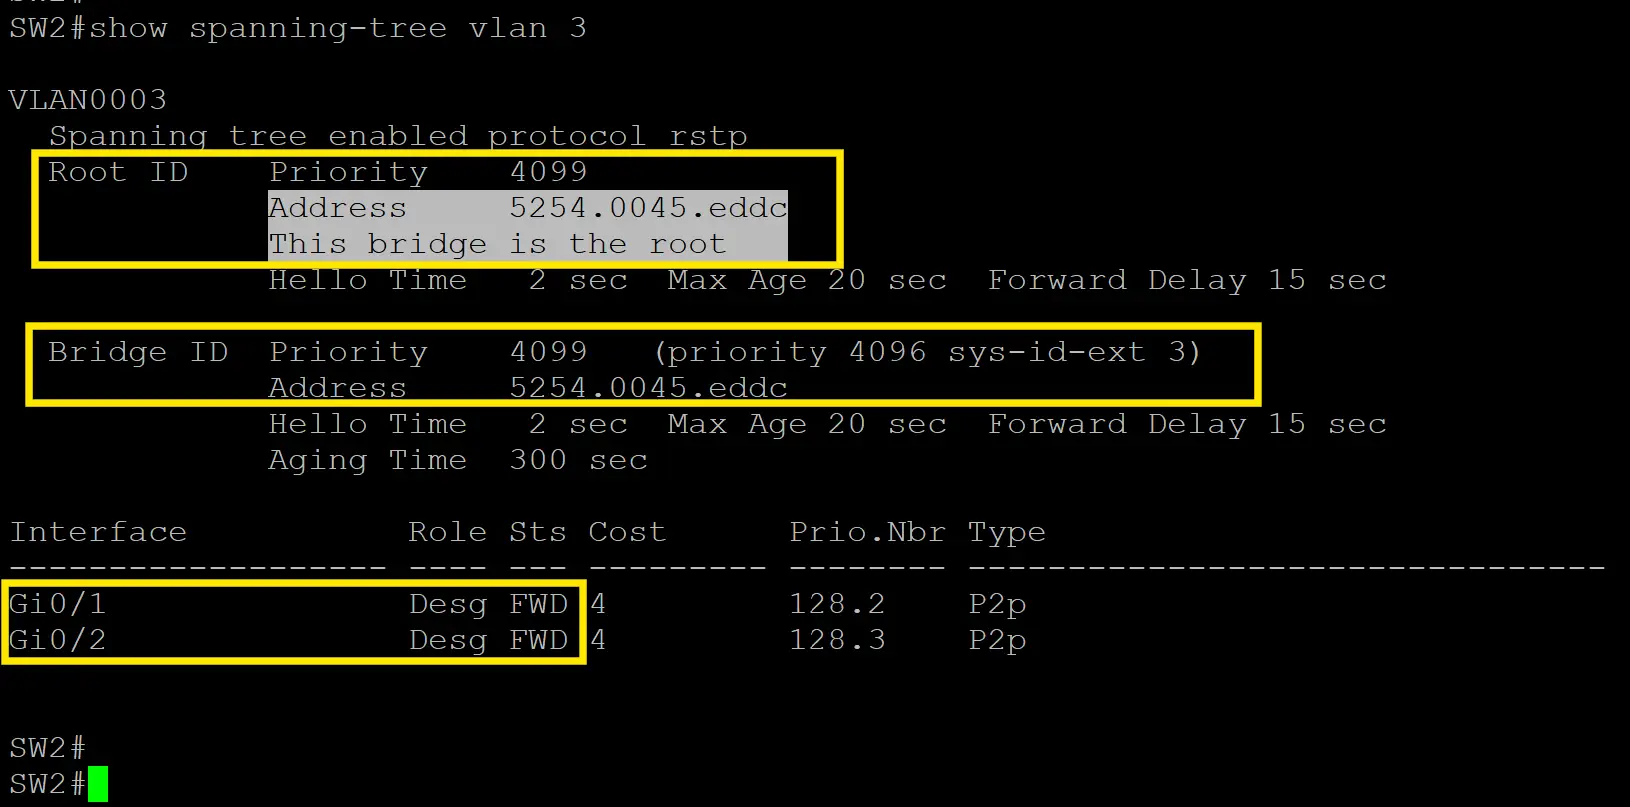
Terminal output of show spanning-tree vlan 3 on SW2: Root ID priority 4099, address 5254.0045.eddc, noting this bridge is the root; Bridge ID matches with priority 4096 sys-id-ext 3. Interfaces Gi0/1 and Gi0/2 are both role Desg, status FWD, cost 4, type P2p.
show spanning-tree vlan 3 output on SW2
Achievable
 

Here, SW2 is the Root Bridge for the VLAN 3 STP instance, and SW2 will declare “This bridge is the root” for VLAN 3.

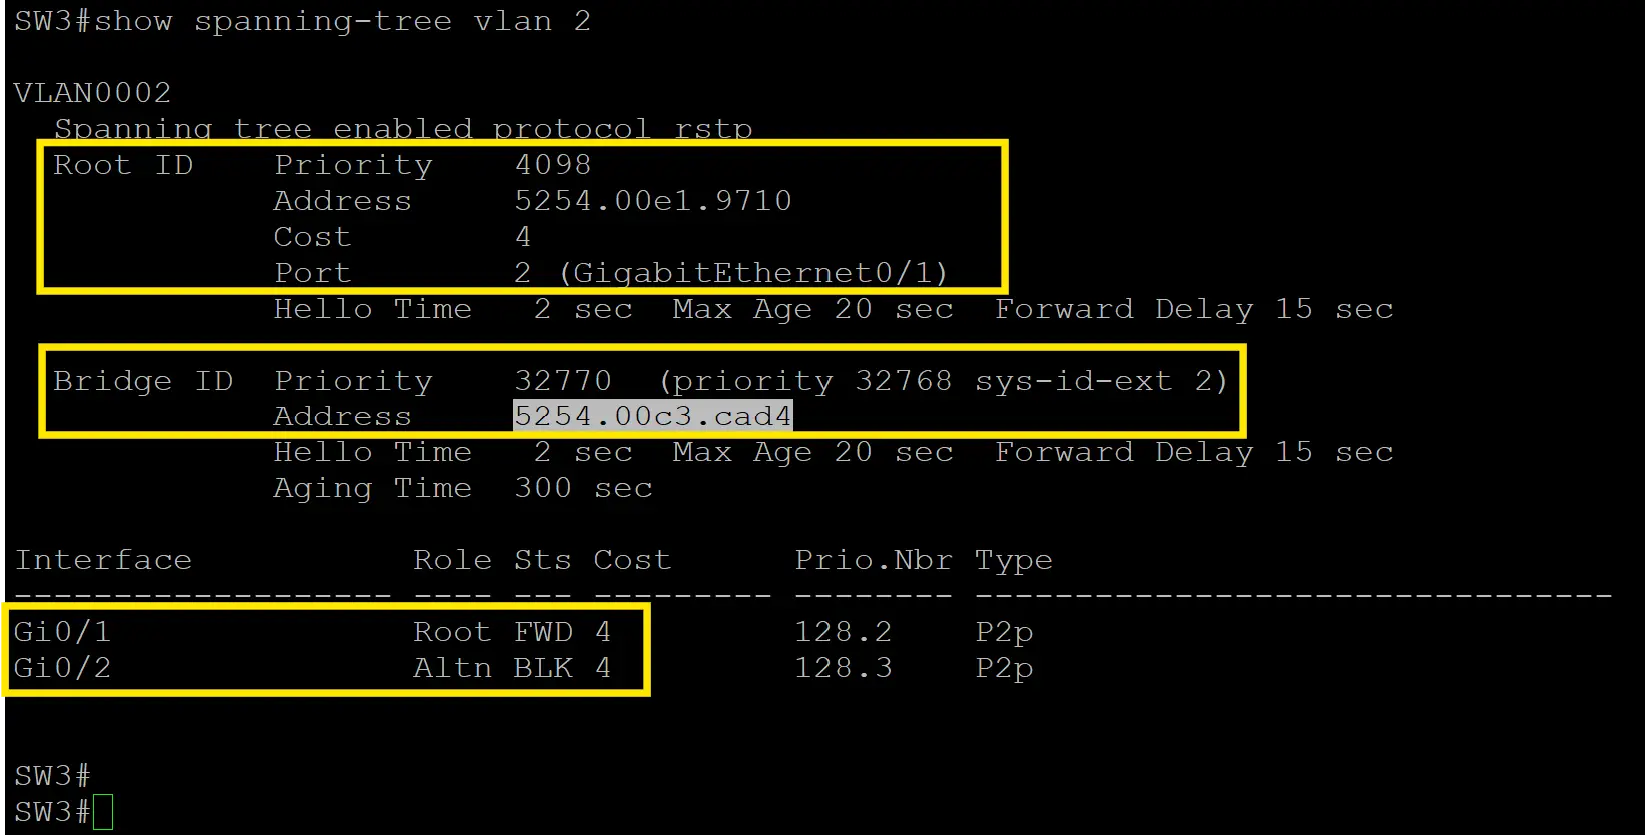
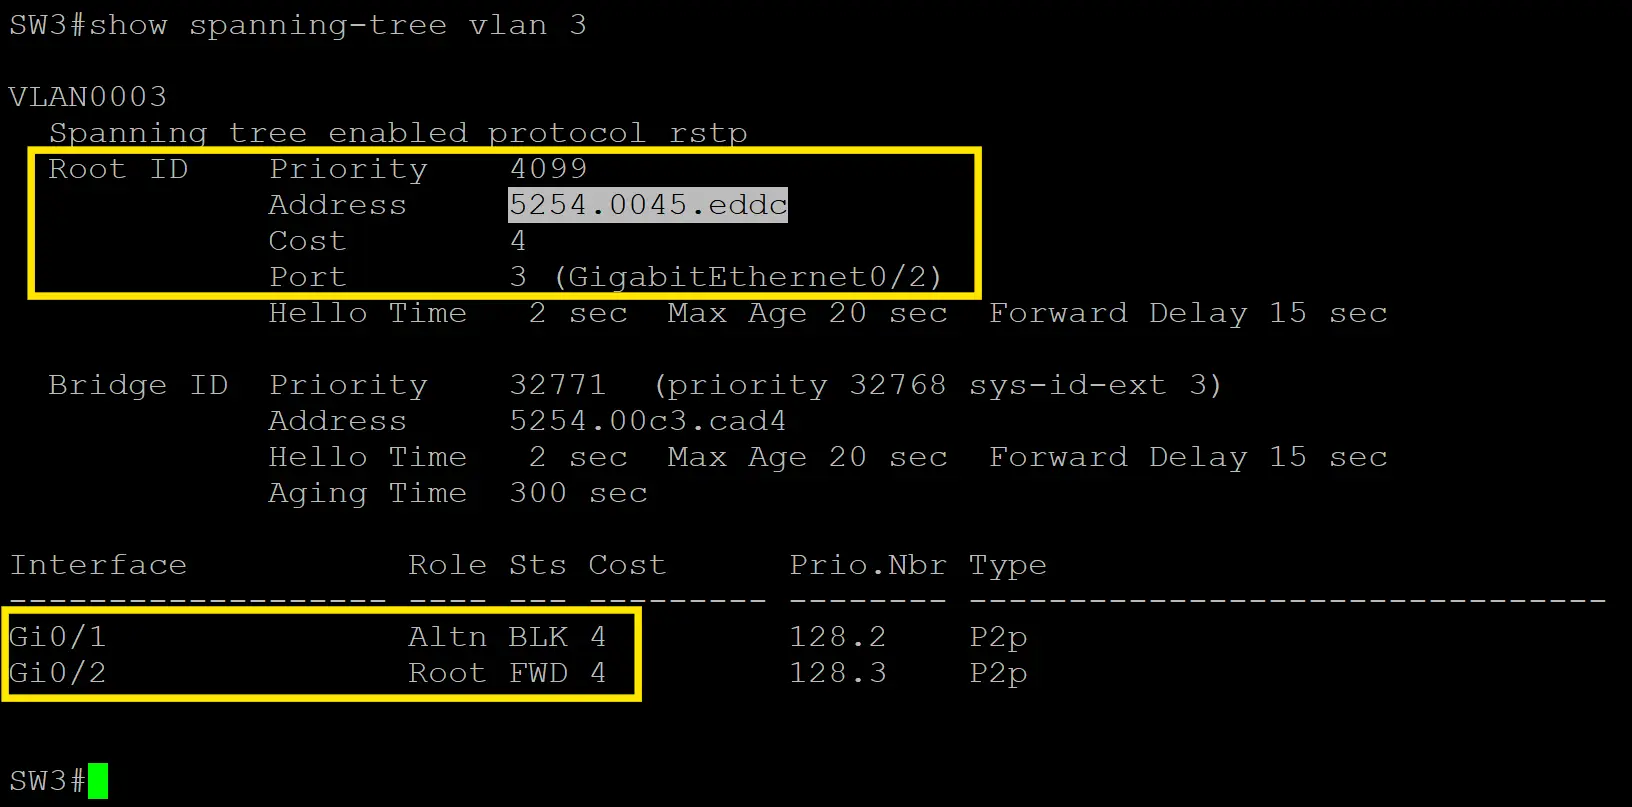
Verify the result from SW3

From SW3’s perspective, the root and alternate ports should match the intended design, and SW3 should not be the root bridge for either VLAN.

SW3 show spanning-tree vlan 2 output: Root ID priority 4098, address 5254.00e1.9710, cost 4 via port Gi0/1; Bridge ID priority 32770, address 5254.00c3.cad4. Interface Gi0/1 is Root, FWD, cost 4; Gi0/2 is Alternate, BLK, cost 4.
show spanning-tree vlan 2 output on SW3
Achievable
 

SW3 show spanning-tree vlan 3 output: Root ID priority 4099, address 5254.0045.eddc, cost 4, root port GigabitEthernet0/2; Bridge ID priority 32771. Interface table shows Gi0/1 as Alternate/Blocking and Gi0/2 as Root/Forwarding, both cost 4.
show spanning-tree vlan 3 output on SW3
Achievable

A simpler root bridge configuration method

There’s also a simpler way to configure primary and secondary root bridges. Cisco provides commands that automatically lower the bridge priority.

On the switch you want as the Primary Root Bridge, enter in global configuration mode:

spanning-tree vlan [VLAN ID] root primary

This automatically lowers the bridge priority to 24576, which is lower than the default (32768), making it preferred.

On the switch you want as the Secondary Root Bridge, enter in global configuration mode:

spanning-tree vlan [VLAN ID] root secondary

This automatically lowers the bridge priority to 28672, which is 4096 higher than the primary value. That makes it less preferred than the primary, but still preferred over a default-priority switch.

Configuring Etherchannels

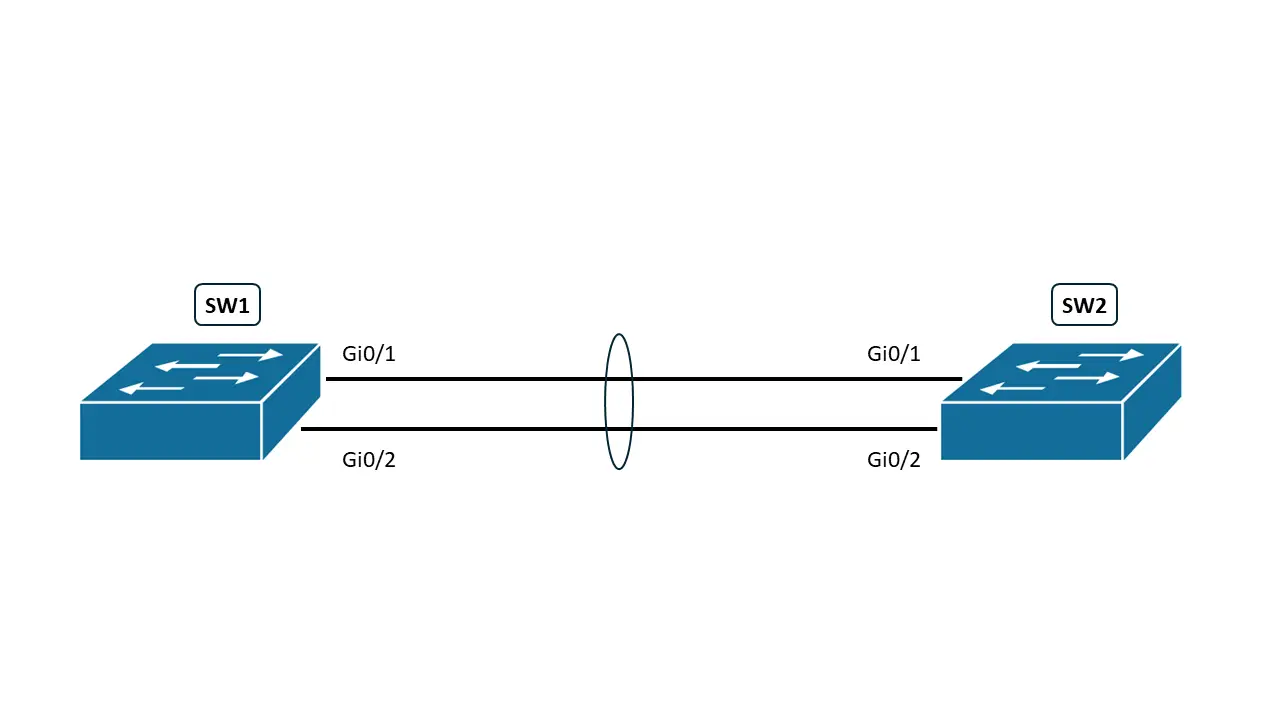
Now consider a scenario where two switches have redundant links between them, and you need to configure an LACP EtherChannel. In this setup:

SW1 and SW2 are connected by two parallel links, Gi0/1 to Gi0/1 and Gi0/2 to Gi0/2, bundled together into a single logical EtherChannel between the switches.
Two switches forming an Etherchannel
Achievable
 

  • SW1 will be the active LACP neighbor.
  • SW2 will be the passive LACP neighbor (it waits for LACP packets from SW1 to negotiate the channel).

For this example, you’ll manually create the Port-Channel interface first, then add the physical interfaces as members.

Create the Port-Channel interface

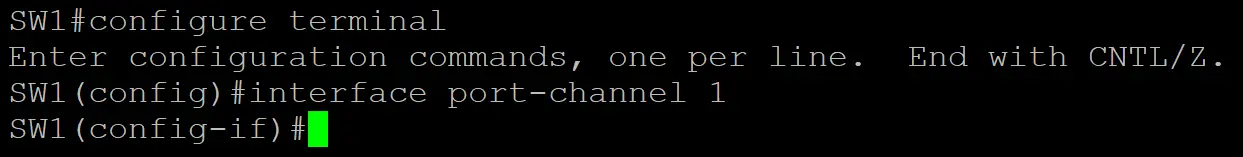
First, create the logical Port-Channel interface that will bundle the physical links. In global configuration mode:

interface port-channel 1

CLI session on SW1: configure terminal enters global config mode, then interface port-channel 1 creates the logical port-channel interface, moving the prompt to SW1(config-if)#
Creating the logical port-channel interface
Achievable

Add member interfaces on SW1

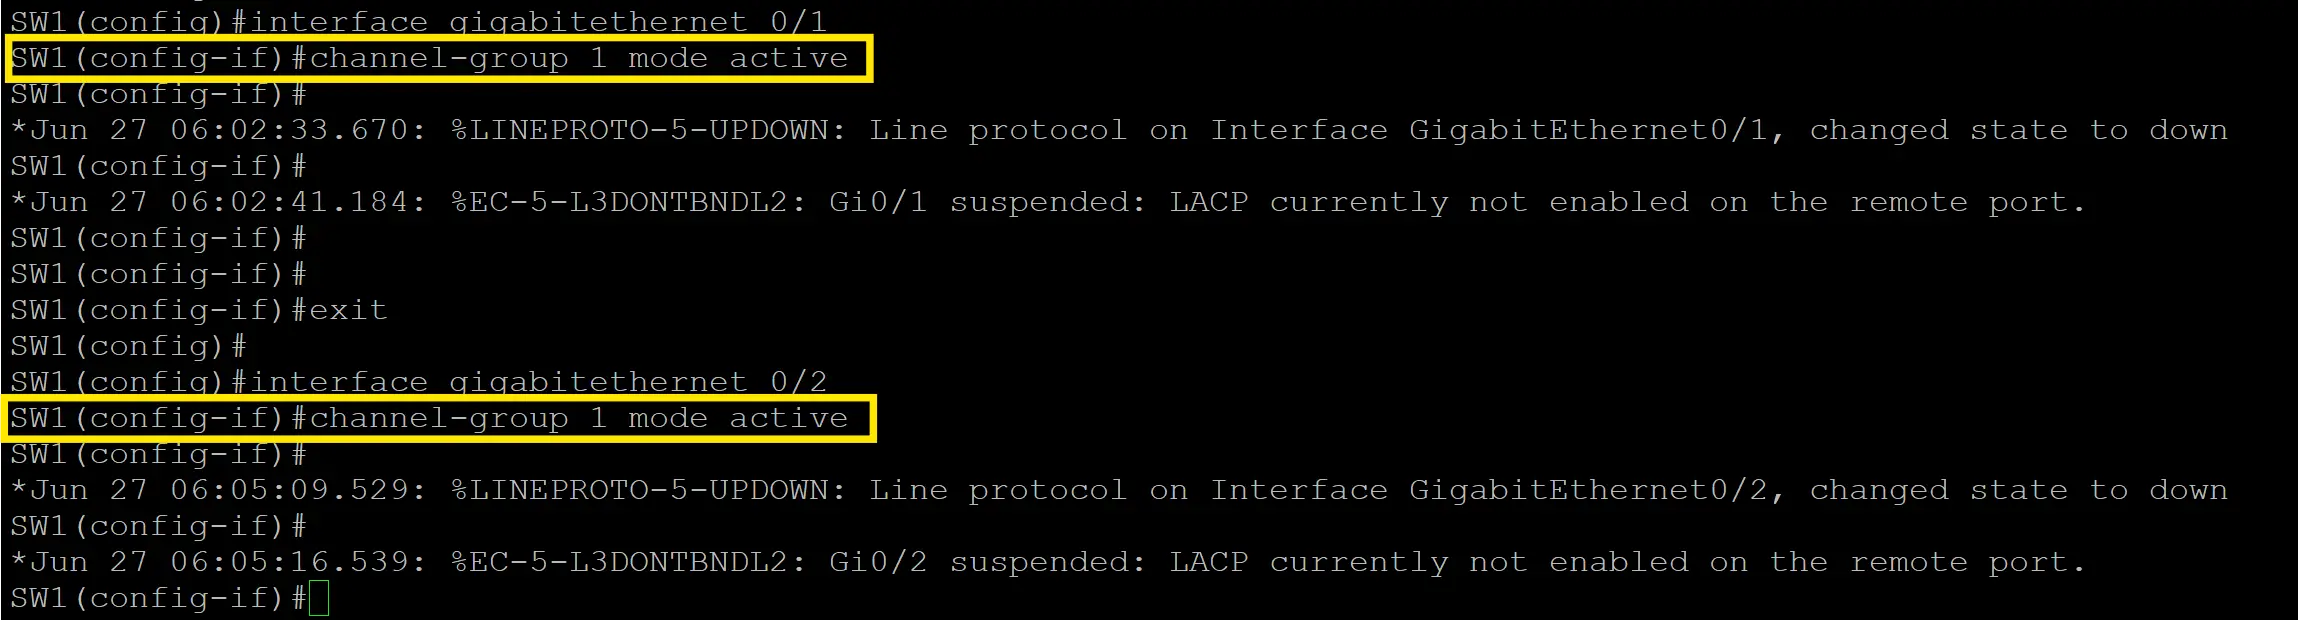
Next, configure each member port (GigabitEthernet 0/1 and GigabitEthernet 0/2) so they join the EtherChannel.

Remember that each member of an Etherchannel must have idendical configurations, therefore, it is best to make sure that the interfaces have their default configurations.

On SW1, under both GigabitEthernet 0/1 and GigabitEthernet 0/2, add:

channel-group 1 mode active

SW1 CLI output showing channel-group 1 mode active applied to interfaces Gi0/1 and Gi0/2, with each link going down and a message that Gi0/1 and Gi0/2 are suspended because LACP is not enabled on the remote port.
Adding GigabitEthernet 0/1 and GigabitEthernet 0/2 as members of Po1
Achievable

It is important to note that the channel-group number must match the Port-Channel interface number that we used when we created it. Otherwise, another Port-Channel interface would be created using the channel-group number that was referenced under the physical interface.

Verify EtherChannel status on SW1

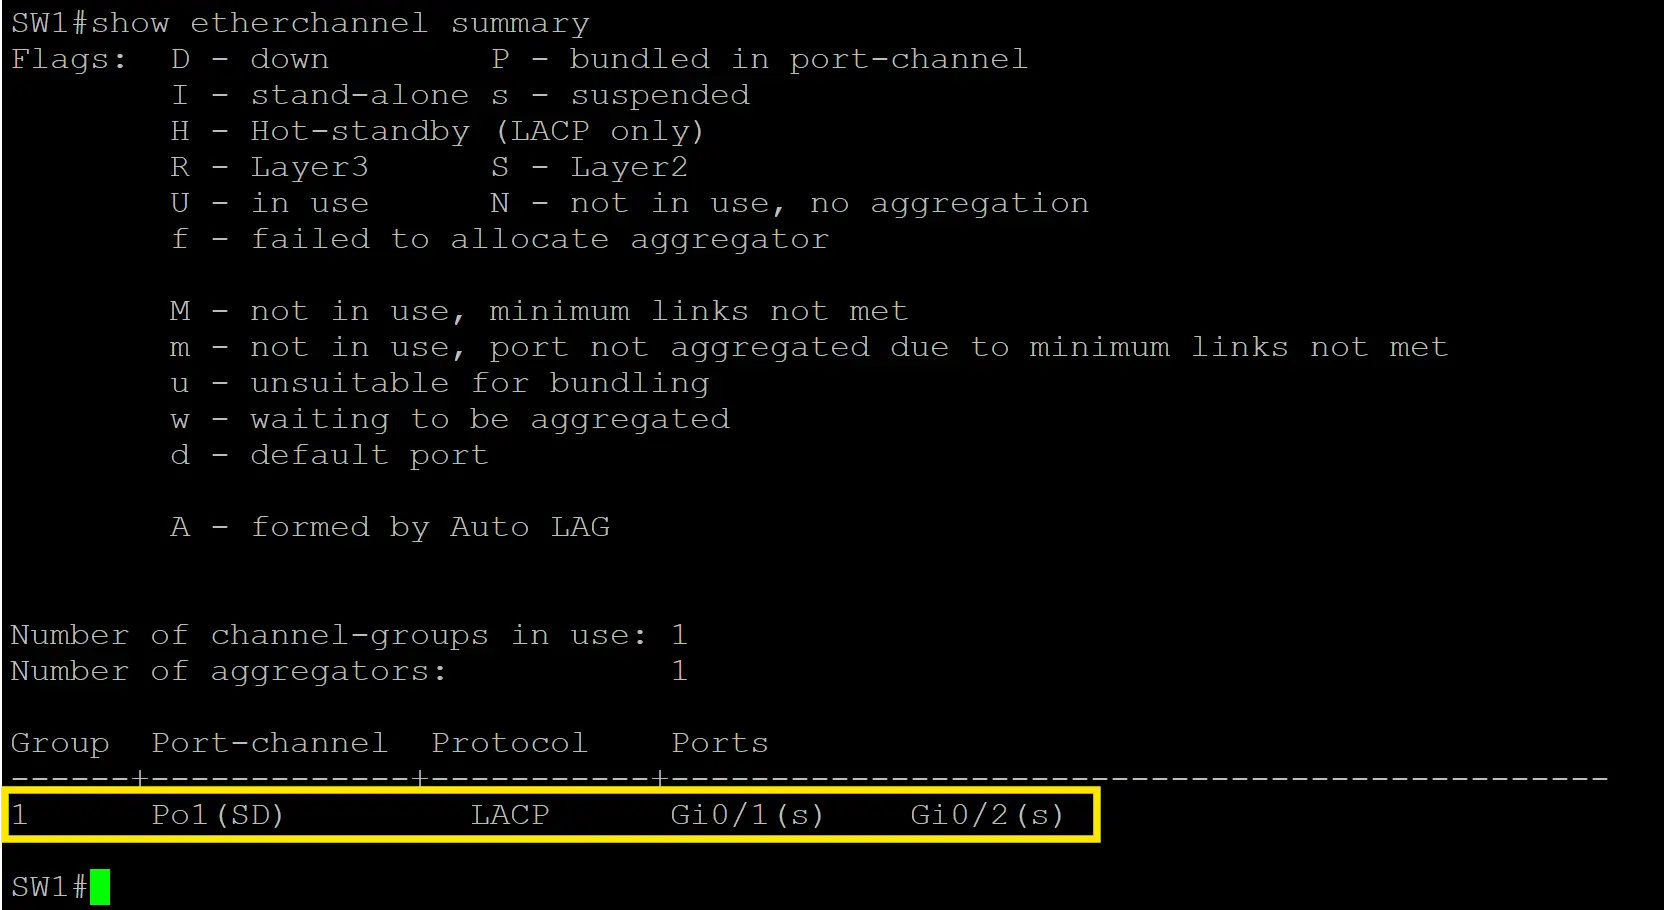
To verify membership and status, run:

show etherchannel summary

SW1 show etherchannel summary output highlights Group 1, Po1(SD), protocol LACP, with ports Gi0/1(s) and Gi0/2(s), indicating both member ports are suspended.
Output of the show etherchannel summary command on SW1
Achievable
 

In the output:

  • The Group number matches the Port-Channel number (1).
  • The Port-Channel interface appears as Po1.
  • The flags show the current state.

For example, SD means:

  • S: Layer 2 EtherChannel
  • D: Down

At this point, it’s down because SW2 hasn’t been configured yet, so LACP hasn’t formed. Once everything is correct, you typically want to see SU.

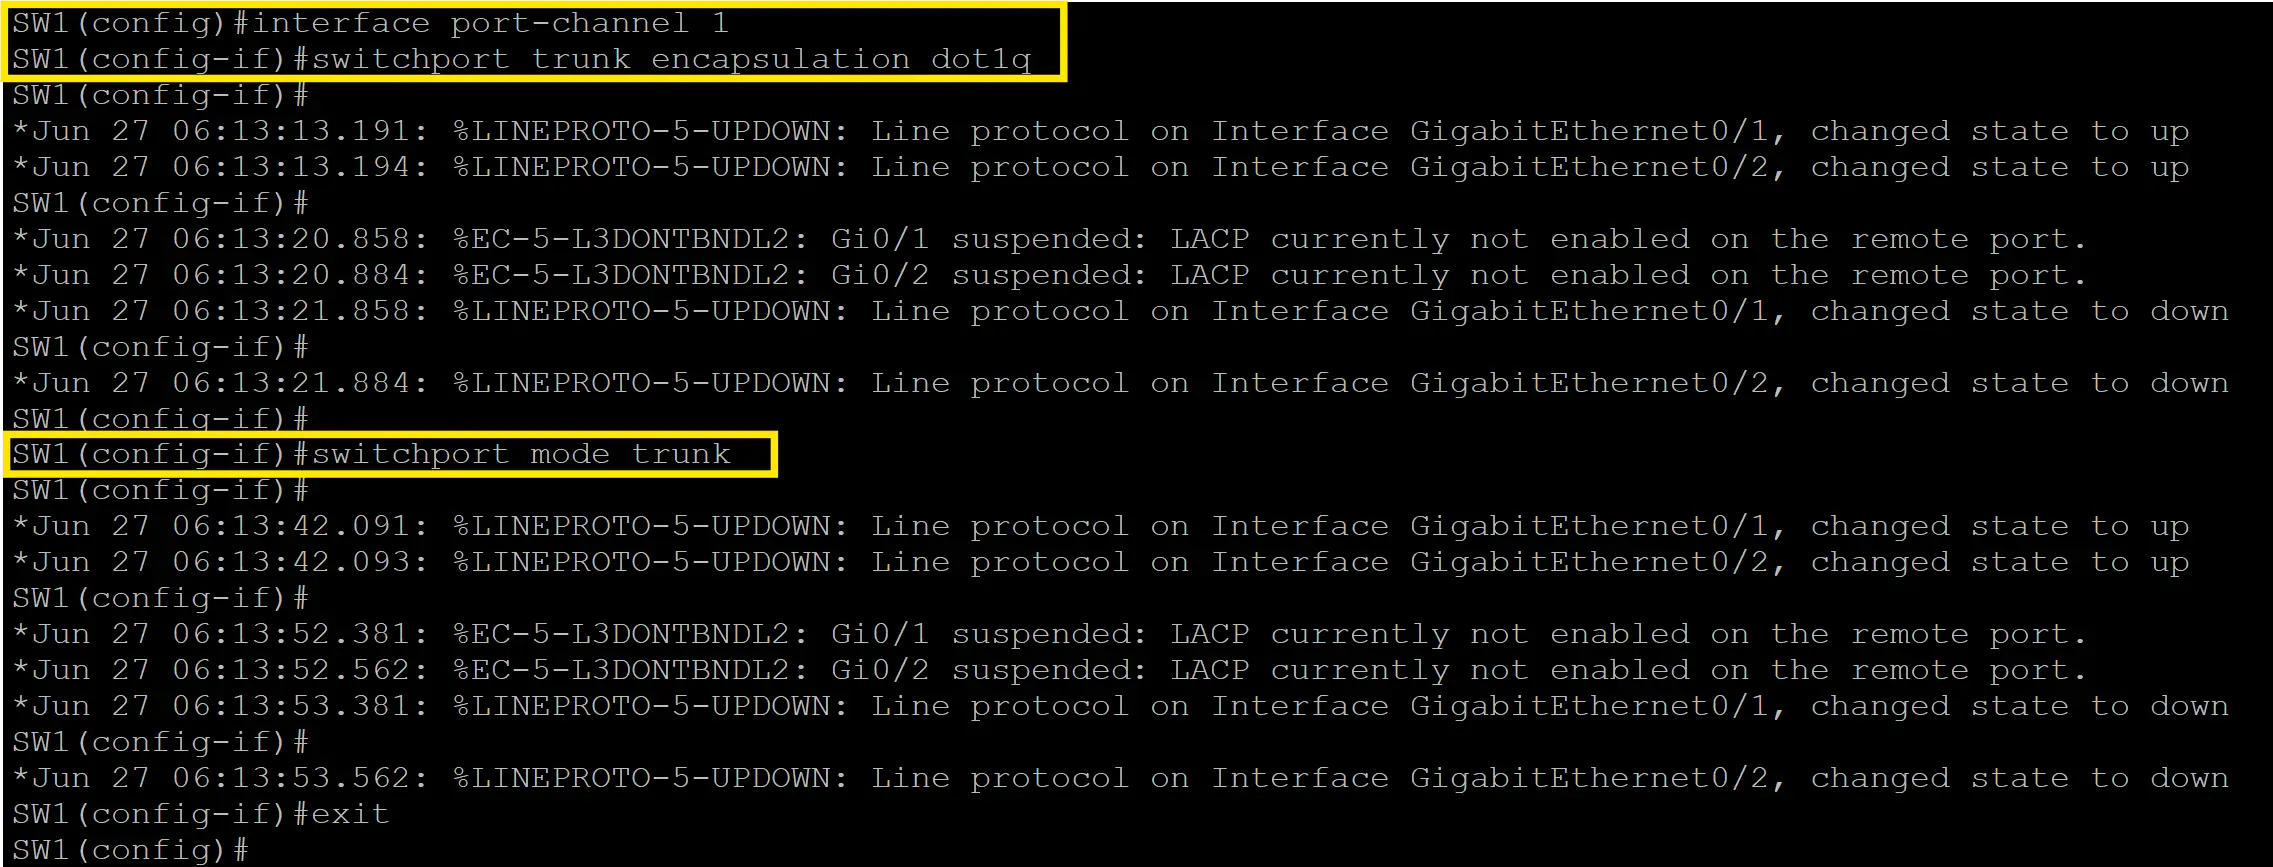
Configure the Port-Channel as a trunk

If you want the EtherChannel to carry multiple VLANs, configure it as a trunk. After an EtherChannel is created, make configuration changes under the Port-Channel interface, and the switch replicates them to the member ports.

SW1 CLI: after setting interface port-channel 1 to switchport trunk encapsulation dot1q and switchport mode trunk, Gi0/1 and Gi0/2 repeatedly come up then get suspended with EC-5-L3DONTBNDL2 errors, LACP currently not enabled on the remote port, causing their line protocol to go down.
Configuring the Etherchannel as a trunk on SW1
Achievable
 

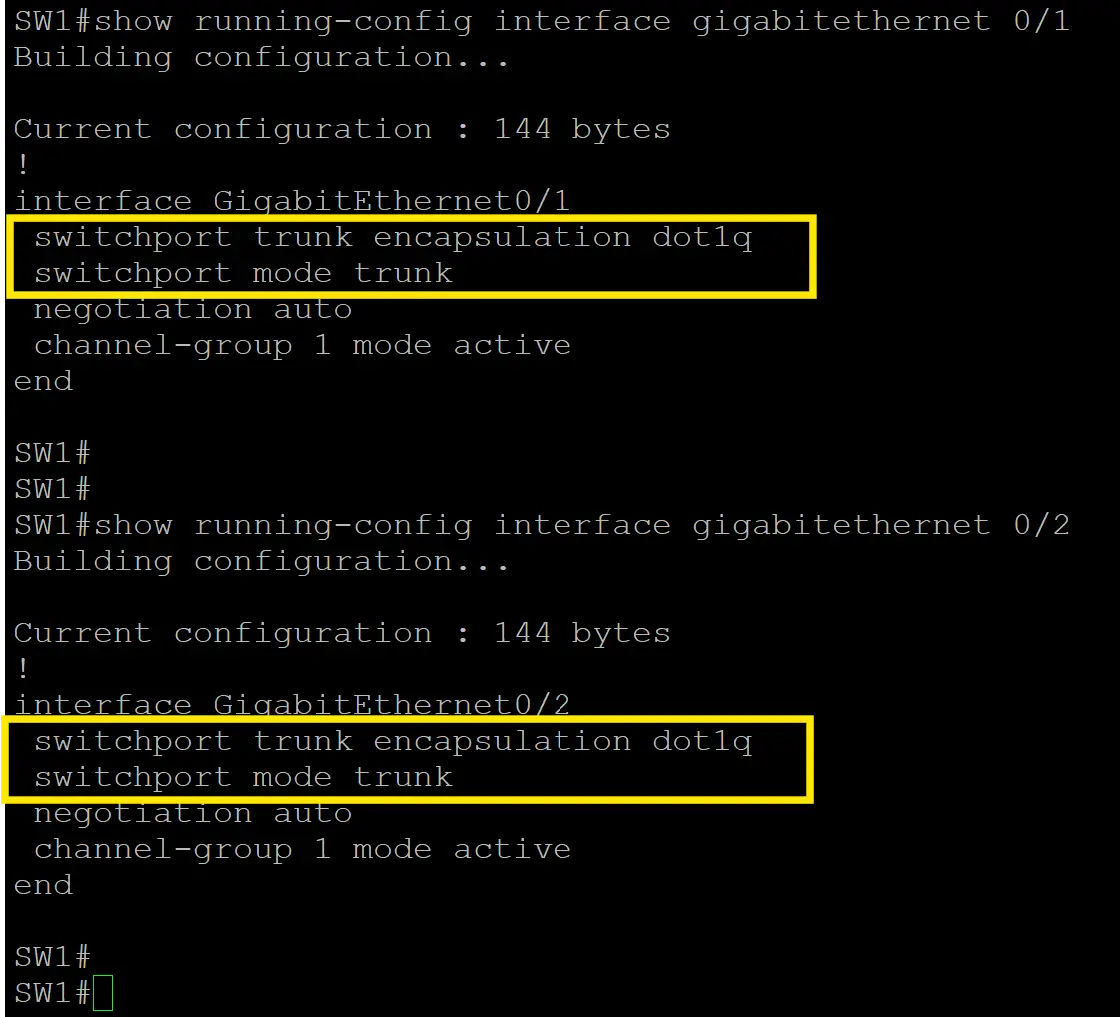
If you check the running configuration, you’ll see the trunk configuration applied to the member ports as well:

SW1 CLI output for show running-config on GigabitEthernet0/1 and 0/2, each highlighting switchport trunk encapsulation dot1q and switchport mode trunk, with both also configured with negotiation auto and channel-group 1 mode active.
Running-Config showing member ports with the trunk configuration
Achievable

Configure SW2 (passive side)

Now configure SW2 with the same overall setup, with one key difference: the member ports use passive mode.

configure terminal

interface port-channel 1 exit

interface gigabitethernet 0/1 channel-group 1 mode passive exit

interface gigabitethernet 0/2 channel-group 1 mode passive exit

interface port-channel 1 switchport mode trunk end

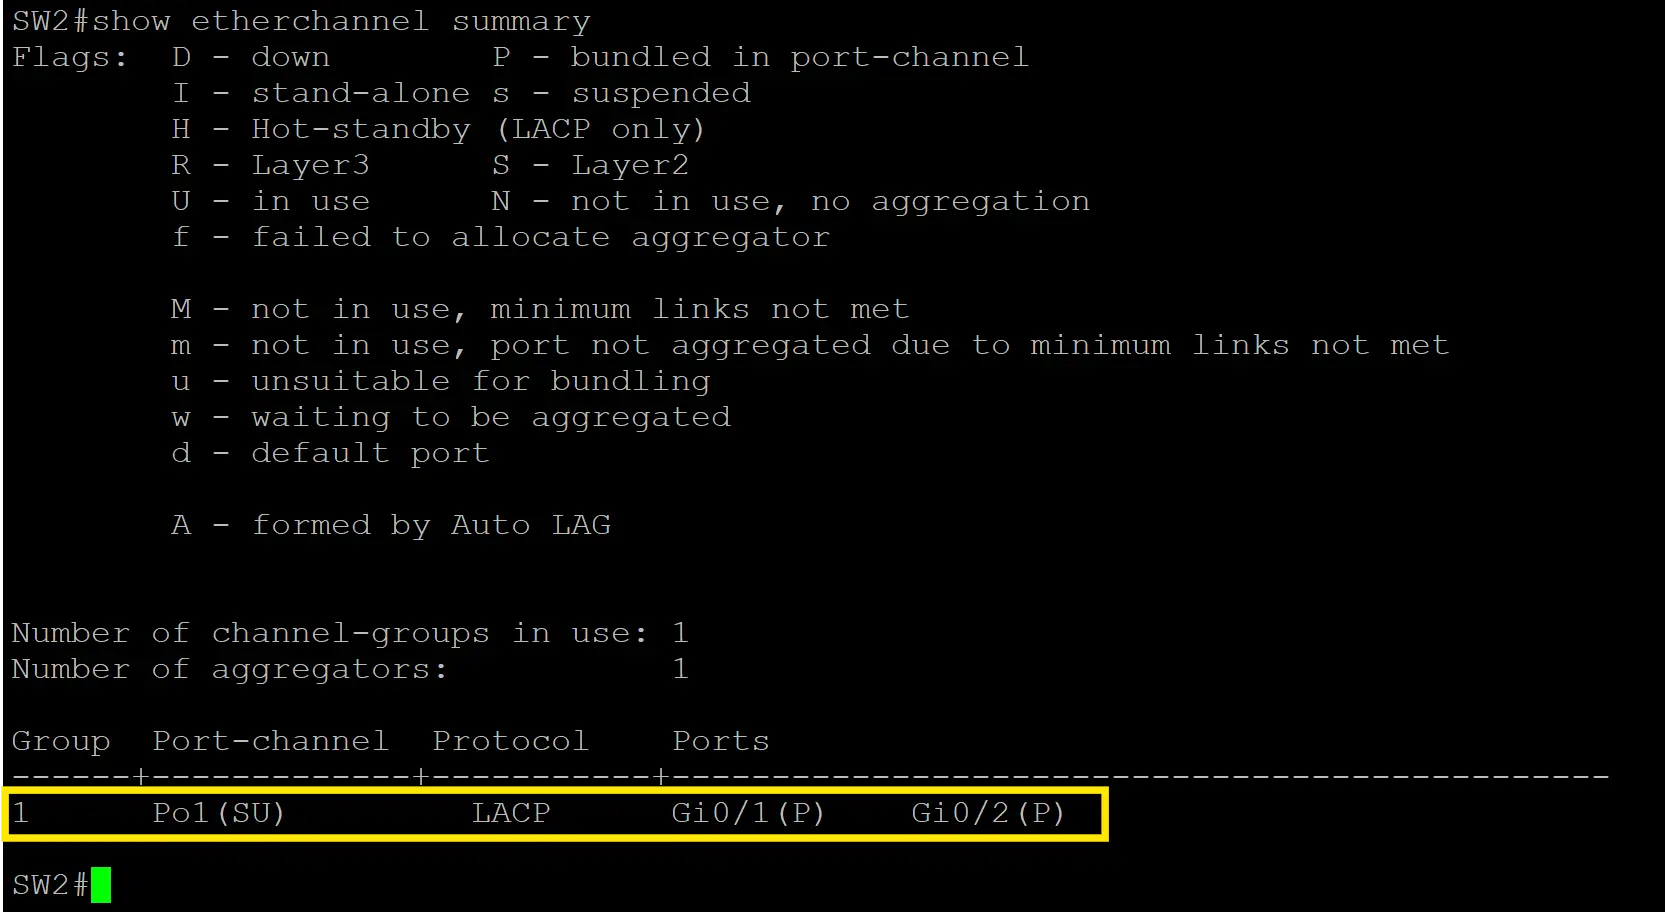
Now check the EtherChannel status on SW2:

SW2 output of show etherchannel summary, highlighting one channel-group: Group 1, Port-channel Po1(SU), Protocol LACP, with member ports Gi0/1(P) and Gi0/2(P), both bundled in the port-channel.
Output of the show etherchannel summary command on SW2
Achievable
 

When the EtherChannel is up, you should see SU, and the member ports should show the P flag (in port-channel). At this point, the EtherChannel between SW1 and SW2 is successfully formed.

Troubleshooting LACP

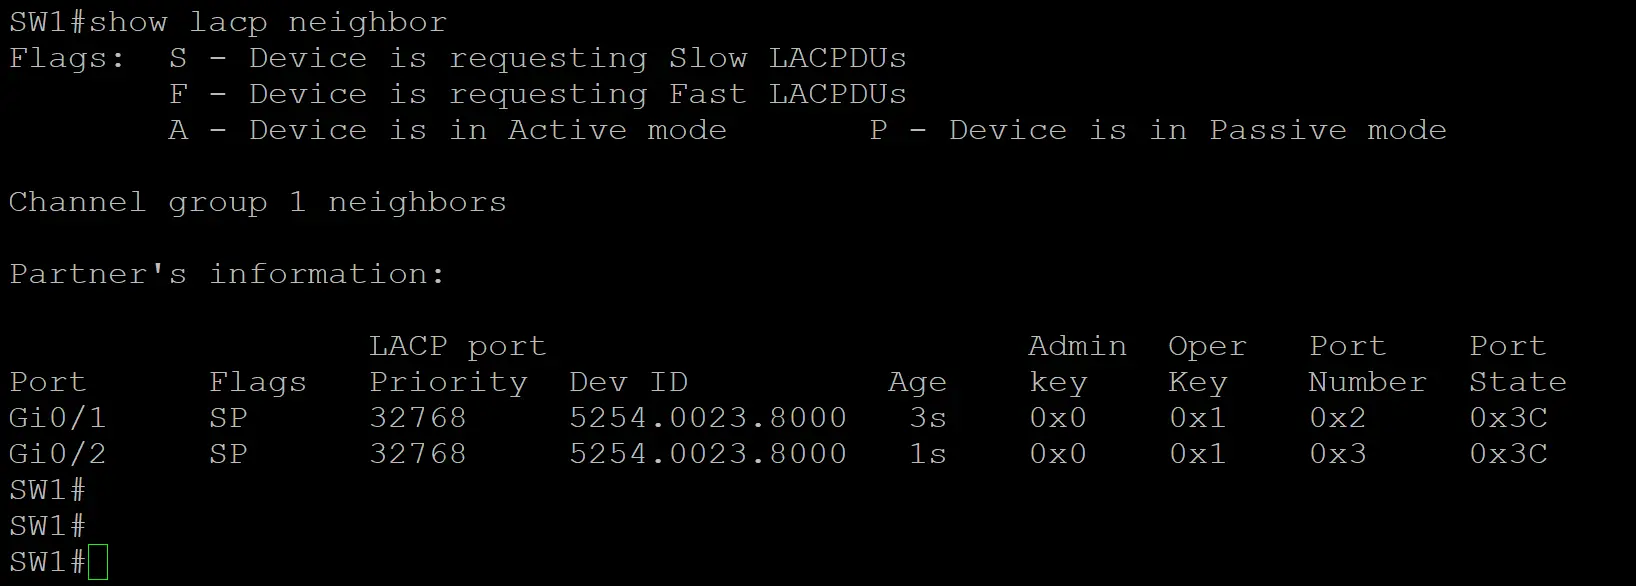
If the LACP EtherChannel isn’t coming up, verify that LACP negotiation is working. In privileged EXEC mode, run:

show lacp neighbor

SW1 output of show lacp neighbor for channel group 1: partner ports Gi0/1 and Gi0/2, flags SP (Slow LACPDUs, Passive mode), device ID 5254.0023.8000, oper key 0x1, port numbers 0x2 and 0x3, and port state 0x3C.
show lacp neighbor command on SW1
Achievable

This command (show lacp neighbor) may not be available in the Cisco Packet Tracer software, so if you are not able to enter this command in Packet Tracer, do not worry as some commands are not available in Packet Tracer. It is available however, in real Cisco IOS images, which are used in the Cisco CML application.

If you run this on “SW1”, the output shows LACP information learned from the neighbor (SW2). One key detail is the P flag under the partner information, which indicates the neighbor is operating in passive mode. Seeing partner information at all is a strong sign that LACP packets are being exchanged and the neighborship has formed.

Also note the mode dependency:

  • If both sides are passive, they won’t form an LACP EtherChannel.
  • At least one side must be active (in this case, SW1).

Rapid PVST+ tuning scenario

  • SW1: Primary Root Bridge for VLAN 2, Secondary for VLAN 3
  • SW2: Primary Root Bridge for VLAN 3, Secondary for VLAN 2
  • SW3: Non-root bridge; correct root/alternate ports per VLAN

Default STP behavior and bridge priority

  • Default bridge priority: 32768
  • Root bridge elected by lowest priority, then lowest MAC address
  • Access switch as root bridge = suboptimal design

Verifying and enabling Rapid PVST+

  • Check STP mode: show spanning-tree
    • “ieee” = legacy 802.1D/PVST+, “rstp” = Rapid PVST+
  • Enable Rapid PVST+: spanning-tree mode rapid-pvst

Setting root bridge priorities per VLAN

  • SW1: spanning-tree vlan 2 priority 4096, vlan 3 priority 8192
  • SW2: spanning-tree vlan 2 priority 8192, vlan 3 priority 4096
  • Priority + VLAN ID = displayed priority (System-ID Extension)

Verifying STP roles and states

  • show spanning-tree vlan [VLAN] to check root/bridge IDs
  • Root bridge ports: Designated, Forwarding state
  • Non-root bridge: root/alternate port roles as designed

Simpler root bridge configuration

  • Primary root: spanning-tree vlan [VLAN] root primary (priority 24576)
  • Secondary root: spanning-tree vlan [VLAN] root secondary (priority 28672)

Configuring EtherChannels (LACP)

  • LACP: SW1 (active), SW2 (passive)
  • Create Port-Channel interface: interface port-channel 1
  • Add member interfaces: channel-group 1 mode active (SW1), mode passive (SW2)
    • Channel-group number must match Port-Channel number

EtherChannel verification and trunking

  • Check status: show etherchannel summary
    • SU = Layer 2, up; SD = Layer 2, down
  • Configure trunking on Port-Channel interface; settings propagate to members

LACP troubleshooting

  • Verify neighbor: show lacp neighbor
    • P flag = passive mode neighbor
  • Both sides passive: EtherChannel will not form
  • At least one side must be active for LACP negotiation

Sign up for free to take 5 quiz questions on this topic

Previous
Next  | 3.1.1 IPv4 addressing
All rights reserved ©2016 - 2026 Achievable, Inc.

How to configure Rapid PVST+ and Etherchannels

Rapid PVST+ tuning

Although Spanning Tree is enabled by default on Cisco switches, the default behavior isn’t always what you want in a real network. STP usually needs some tuning so the root bridge and forwarding paths line up with your design.

Here’s the scenario: three switches are connected to each other with trunk links - SW1, SW2, and SW3. SW1 and SW2 are distribution switches, and SW3 is the access switch.


In this design:

  • SW1 should be the Primary Root Bridge for VLAN 2 and the Secondary (backup) Root Bridge for VLAN 3.
  • SW2 should be the Primary Root Bridge for VLAN 3 and the Secondary Root Bridge for VLAN 2.

That way, SW1 and SW2 back each other up if one fails.

This makes SW3 the Non-Root Bridge. For VLAN 2, SW3’s:

  • Root Port should be GigabitEthernet 0/1.
  • GigabitEthernet 0/2 should be an Alternate Port.

Which port on SW3 should be the Root Port for VLAN 3 traffic and which port should be the Alternate Port?

(spoiler)
  • SW3’s GigabitEthernet 0/2 should be the Root Port for VLAN 3 traffic
  • SW3’s GigabitEthernet 0/1 should be the Alternate Port for VLAN 3 traffic

If you leave all three switches at their default STP settings, they might not converge the way you intend. With the default bridge priority on all switches, the root bridge election comes down to the switch with the lowest base MAC address.

What is the default Bridge Priority value on all Switches running STP?

(spoiler)

32768

Now consider what happens if SW3 has the lowest base MAC address. SW3 could become the root bridge, which is usually not what you want in a hierarchical design.

Having an access switch as the root bridge for your LAN can create bottlenecks and suboptimal traffic paths.

To prevent that, you configure SW1 and SW2 so they reliably become the root bridges for their intended VLANs.

Verify and enable Rapid PVST+

Before tuning priorities, make sure the switches are running Rapid PVST+. Some switches may still be using the legacy STP version (802.1D / PVST+) by default.

To verify the current STP mode, use:

show spanning-tree


This output also shows STP information per VLAN. With Cisco Per-VLAN Spanning Tree, each VLAN runs its own STP instance.

In the output, look for the line:

  • Spanning tree enabled protocol

If you see ieee, the switch is running the legacy STP mode (802.1D / PVST+). In this scenario, you want to change all three switches to Rapid PVST+.

To enable Rapid PVST+, go to global configuration mode and enter:

spanning-tree mode rapid-pvst


If you run show spanning-tree again, you should now see the protocol listed as rstp, which indicates Rapid PVST+.

This should be configured on all 3 switches.

Set root bridge priorities per VLAN

Now you can tune SW1 and SW2 so they become the intended root bridges.

  • Make SW1 the Primary Root Bridge for VLAN 2 and the Secondary Root Bridge for VLAN 3.
  • Make SW2 the Primary Root Bridge for VLAN 3 and the Secondary Root Bridge for VLAN 2.

On SW1, in global configuration mode, set:

spanning-tree vlan 2 priority 4096 spanning-tree vlan 3 priority 8192

On SW2, do the opposite:

spanning-tree vlan 2 priority 8192 spanning-tree vlan 3 priority 4096

Verify the result on SW1 and SW2

To check the VLAN 2 STP instance on SW1 and SW2, use:

  • show spanning-tree vlan 2

This filters the output so you only see the VLAN 2 STP instance.


In the output:

  • The Root ID section shows which switch is the root bridge for that VLAN.
  • The Bridge ID section shows the local switch’s STP identity.

On SW1, you’ll see it declare “This bridge is the root” for VLAN 2. You’ll also notice:

  • The configured priority was 4096.
  • The displayed priority becomes 4098 because the System-ID Extension adds the VLAN number (here, 4096 + 2).

Because SW1 is the root bridge for VLAN 2, its active ports for that VLAN take the Designated Port role (Desg) and are in the Forwarding state (FWD).

On SW2, the Root ID shows SW1’s base MAC address as the root for VLAN 2. SW2’s Bridge ID differs from the Root ID because SW2 is not the root bridge for VLAN 2.


If you run the same check for VLAN 3, you should see the opposite behavior:


Here, SW2 is the Root Bridge for the VLAN 3 STP instance, and SW2 will declare “This bridge is the root” for VLAN 3.

Verify the result from SW3

From SW3’s perspective, the root and alternate ports should match the intended design, and SW3 should not be the root bridge for either VLAN.


A simpler root bridge configuration method

There’s also a simpler way to configure primary and secondary root bridges. Cisco provides commands that automatically lower the bridge priority.

On the switch you want as the Primary Root Bridge, enter in global configuration mode:

spanning-tree vlan [VLAN ID] root primary

This automatically lowers the bridge priority to 24576, which is lower than the default (32768), making it preferred.

On the switch you want as the Secondary Root Bridge, enter in global configuration mode:

spanning-tree vlan [VLAN ID] root secondary

This automatically lowers the bridge priority to 28672, which is 4096 higher than the primary value. That makes it less preferred than the primary, but still preferred over a default-priority switch.

Configuring Etherchannels

Now consider a scenario where two switches have redundant links between them, and you need to configure an LACP EtherChannel. In this setup:


  • SW1 will be the active LACP neighbor.
  • SW2 will be the passive LACP neighbor (it waits for LACP packets from SW1 to negotiate the channel).

For this example, you’ll manually create the Port-Channel interface first, then add the physical interfaces as members.

Create the Port-Channel interface

First, create the logical Port-Channel interface that will bundle the physical links. In global configuration mode:

interface port-channel 1

Add member interfaces on SW1

Next, configure each member port (GigabitEthernet 0/1 and GigabitEthernet 0/2) so they join the EtherChannel.

Remember that each member of an Etherchannel must have idendical configurations, therefore, it is best to make sure that the interfaces have their default configurations.

On SW1, under both GigabitEthernet 0/1 and GigabitEthernet 0/2, add:

channel-group 1 mode active

It is important to note that the channel-group number must match the Port-Channel interface number that we used when we created it. Otherwise, another Port-Channel interface would be created using the channel-group number that was referenced under the physical interface.

Verify EtherChannel status on SW1

To verify membership and status, run:

show etherchannel summary


In the output:

  • The Group number matches the Port-Channel number (1).
  • The Port-Channel interface appears as Po1.
  • The flags show the current state.

For example, SD means:

  • S: Layer 2 EtherChannel
  • D: Down

At this point, it’s down because SW2 hasn’t been configured yet, so LACP hasn’t formed. Once everything is correct, you typically want to see SU.

Configure the Port-Channel as a trunk

If you want the EtherChannel to carry multiple VLANs, configure it as a trunk. After an EtherChannel is created, make configuration changes under the Port-Channel interface, and the switch replicates them to the member ports.


If you check the running configuration, you’ll see the trunk configuration applied to the member ports as well:

Configure SW2 (passive side)

Now configure SW2 with the same overall setup, with one key difference: the member ports use passive mode.

configure terminal

interface port-channel 1 exit

interface gigabitethernet 0/1 channel-group 1 mode passive exit

interface gigabitethernet 0/2 channel-group 1 mode passive exit

interface port-channel 1 switchport mode trunk end

Now check the EtherChannel status on SW2:


When the EtherChannel is up, you should see SU, and the member ports should show the P flag (in port-channel). At this point, the EtherChannel between SW1 and SW2 is successfully formed.

Troubleshooting LACP

If the LACP EtherChannel isn’t coming up, verify that LACP negotiation is working. In privileged EXEC mode, run:

show lacp neighbor

This command (show lacp neighbor) may not be available in the Cisco Packet Tracer software, so if you are not able to enter this command in Packet Tracer, do not worry as some commands are not available in Packet Tracer. It is available however, in real Cisco IOS images, which are used in the Cisco CML application.

If you run this on “SW1”, the output shows LACP information learned from the neighbor (SW2). One key detail is the P flag under the partner information, which indicates the neighbor is operating in passive mode. Seeing partner information at all is a strong sign that LACP packets are being exchanged and the neighborship has formed.

Also note the mode dependency:

  • If both sides are passive, they won’t form an LACP EtherChannel.
  • At least one side must be active (in this case, SW1).
Key points

Rapid PVST+ tuning scenario

  • SW1: Primary Root Bridge for VLAN 2, Secondary for VLAN 3
  • SW2: Primary Root Bridge for VLAN 3, Secondary for VLAN 2
  • SW3: Non-root bridge; correct root/alternate ports per VLAN

Default STP behavior and bridge priority

  • Default bridge priority: 32768
  • Root bridge elected by lowest priority, then lowest MAC address
  • Access switch as root bridge = suboptimal design

Verifying and enabling Rapid PVST+

  • Check STP mode: show spanning-tree
    • “ieee” = legacy 802.1D/PVST+, “rstp” = Rapid PVST+
  • Enable Rapid PVST+: spanning-tree mode rapid-pvst

Setting root bridge priorities per VLAN

  • SW1: spanning-tree vlan 2 priority 4096, vlan 3 priority 8192
  • SW2: spanning-tree vlan 2 priority 8192, vlan 3 priority 4096
  • Priority + VLAN ID = displayed priority (System-ID Extension)

Verifying STP roles and states

  • show spanning-tree vlan [VLAN] to check root/bridge IDs
  • Root bridge ports: Designated, Forwarding state
  • Non-root bridge: root/alternate port roles as designed

Simpler root bridge configuration

  • Primary root: spanning-tree vlan [VLAN] root primary (priority 24576)
  • Secondary root: spanning-tree vlan [VLAN] root secondary (priority 28672)

Configuring EtherChannels (LACP)

  • LACP: SW1 (active), SW2 (passive)
  • Create Port-Channel interface: interface port-channel 1
  • Add member interfaces: channel-group 1 mode active (SW1), mode passive (SW2)
    • Channel-group number must match Port-Channel number

EtherChannel verification and trunking

  • Check status: show etherchannel summary
    • SU = Layer 2, up; SD = Layer 2, down
  • Configure trunking on Port-Channel interface; settings propagate to members

LACP troubleshooting

  • Verify neighbor: show lacp neighbor
    • P flag = passive mode neighbor
  • Both sides passive: EtherChannel will not form
  • At least one side must be active for LACP negotiation

More from Configuring Cisco Switches

  • Introduction to Cisco's Internetworking Operating System (IOS)
  • MAC address table & VLAN configuration
  • The Voice VLAN and Layer 1 troubleshooting