


This browser is too old to run Achievable.

Update it, or open this page in a current version of Chrome, Safari, Firefox or Edge. On an iPhone or iPad, update iOS: every browser there runs on the version of Safari that comes with it.

Achievable logoAchievable logo
CCNA
Sign in
Sign up
Purchase
Textbook
Practice exams
Support
How it works
Resources
Exam catalog
Mountain with a flag at the peak
Textbook
Introduction
1. Introduction to networking
2. Administering Ethernet LANs
2.1 Wired network access
2.2 Hosts communicating on a Local Area Network
2.3 Virtual LANs (VLANs)
2.4 Layer 2 link redundancy
2.5 Configuring Cisco Switches
3. IP connectivity
4. Network services
5. IPv6
6. Wireless networking
7. Network management and administering network devices
8. Network security fundamentals
9. Network automation and programmability
Wrapping up
Achievable logoAchievable logo
2.3 Virtual LANs (VLANs)
Achievable CCNA
2. Administering Ethernet LANs
Our CCNA course is currently in development and is a work-in-progress.

Virtual LANs (VLANs)

10 min read
Font
Discuss
Share
Feedback

In the previous chapter, you learned how hosts discover the MAC address of the host they want to communicate with. They do this by sending an ARP Request in a broadcast frame. If the target host is online and connected to the LAN, it responds directly (unicast) to the sender with an ARP Reply that includes its MAC address.

Broadcasts are useful when you don’t know where a host is on the LAN. They also help switches learn which switchport a host is connected to. However, broadcasts come with an important drawback.

Imagine a very large LAN made up of many interconnected switches, with endpoint devices connected to most (or all) switchports.

What happens when a switch receives a broadcast frame (after learning the source MAC address)?

(spoiler)

The switch makes copies of the broadcast frame and floods it out of every port, except the port on which the frame was received.

This can significantly impact network performance. It also affects endpoints that receive these broadcast copies. Broadcasts are meant for everyone, so every host that receives a broadcast frame must interrupt its CPU (Central Processing Unit) to process the frame. Even if the IP packet inside the frame isn’t destined for that device’s IP address, the device still has to examine and process the frame.

On a large LAN with hundreds or thousands of endpoints, repetitive broadcasts can become a serious burden because every endpoint receives and processes every broadcast frame.

To address this, Ethernet switches introduced a feature that lets you group physical switchports into separate LANs called “Virtual LANs,” or VLANs.

Virtual LANs (VLANs)

A VLAN segments the broadcast boundary. The area in which broadcasts can propagate is called a Broadcast Domain.

By default:

  • All ports on a switch are in the same broadcast domain.
  • That means they’re all on the same LAN.

When you connect one switch to another, you extend the LAN and also extend the broadcast domain.

When you create a VLAN and move switchports into it, those switchports become part of a different broadcast domain. As a result:

  • Broadcasts propagated within one VLAN can’t reach another VLAN.
  • Broadcasts originating within a particular VLAN can only be seen or received by hosts within that same VLAN.

In short; “VLANs segment Broadcast Domains”

Historically, VLANs were especially helpful because endpoint CPUs were more sensitive to periodic broadcasts due to hardware limitations at the time. Modern CPUs are much more capable, but excessive broadcasts can still cause problems.

Today, VLANs are commonly used as a security and segmentation tool: they separate groups of endpoints so only the intended devices can communicate directly and receive each other’s broadcasts.

By default, all switchports are in the Default VLAN, which is VLAN 1. It’s important to know that you cannot create, modify or delete VLAN 1.

If you want to group endpoints into different VLANs, the steps are:

  1. Create the VLAN
  2. Move the switchport(s) into the new VLAN

This process is straightforward. The key detail to remember is that switches associate learned MAC addresses with:

  • the switchport they were learned on, and
  • the VLAN that switchport is configured to be in.

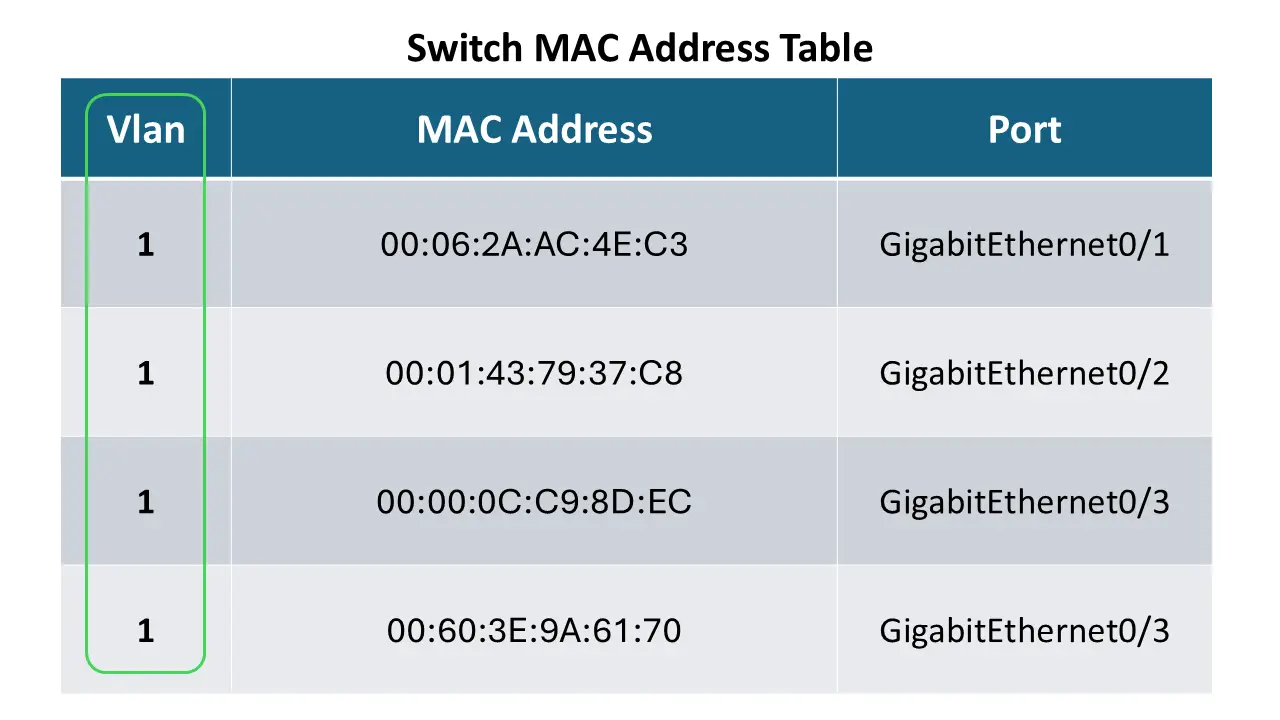
Take the MAC address table example below. Notice that each MAC address entry includes a VLAN and the port where the MAC address was learned. That VLAN value tells you which VLAN the port belongs to.

Switch MAC address table with Vlan, MAC Address, and Port columns, all entries in Vlan 1: 00:06:2A:AC:4E:C3 on GigabitEthernet0/1, 00:01:43:79:37:C8 on Gi0/2, 00:00:0C:C9:8D:EC and 00:60:3E:9A:61:70 both on Gi0/3.
MAC Table displaying VLANs
Achievable
 

Whenever you see “VLAN 1,” that means the switchport is still using its default factory settings and hasn’t been moved into an administratively created VLAN.

Always remember: hosts can only learn the MAC addresses of other hosts within the same VLAN only. That’s because hosts use ARP to discover MAC addresses, and ARP relies on broadcast frames. Since broadcasts from one VLAN can’t reach another VLAN, hosts in a different VLAN never receive the ARP Request and therefore can’t reply.

This doesn’t mean hosts can’t communicate across VLANs. They can, but they need a router (or a Layer 3 switch that can perform routing). We’ll cover that in the routing chapters (IP connectivity).

Let’s take a look at how intra-VLAN communication works in two scenarios:

Scenario 1: Hosts that are connected to a single switch

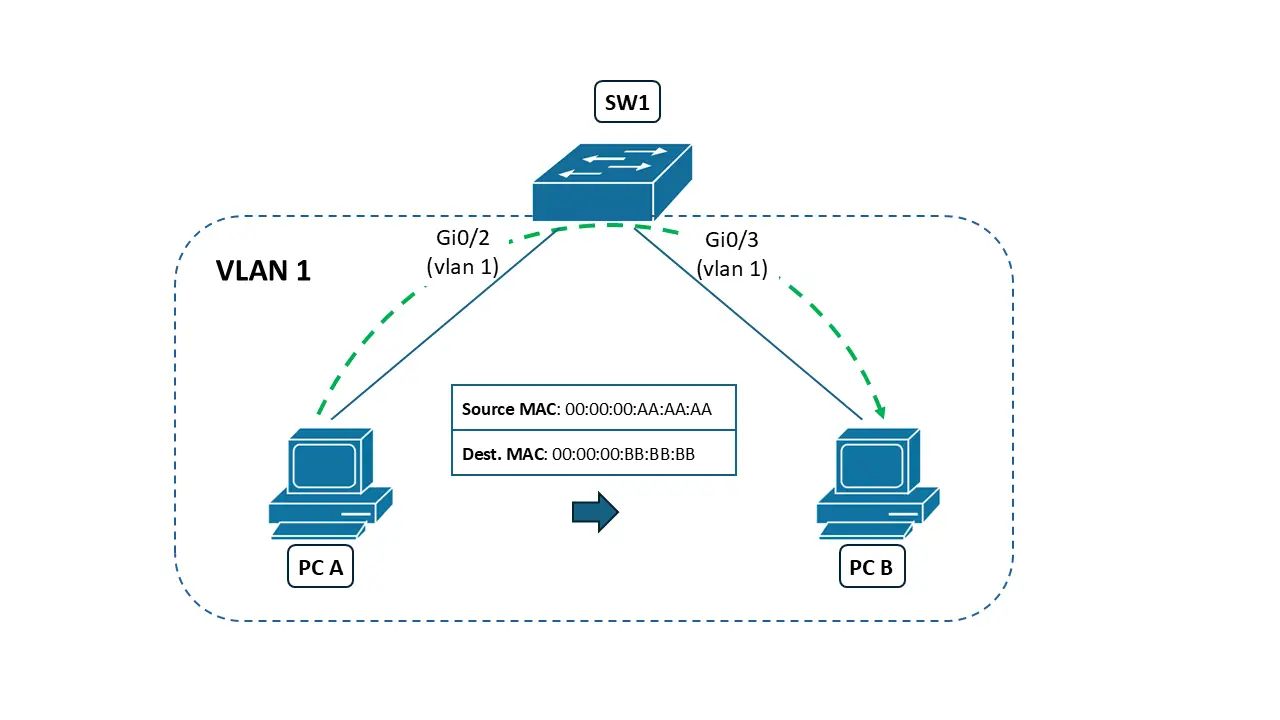
If two hosts are connected to the same switch and their ports are configured in the same VLAN, they can communicate directly.

PC A and PC B, both in VLAN 1, connect to switch SW1 on ports Gi0/2 and Gi0/3. A frame with source MAC 00:00:00:AA:AA:AA and destination MAC 00:00:00:BB:BB:BB travels from PC A through the switch to PC B.
PC A and PC B same switch same vlan
Achievable

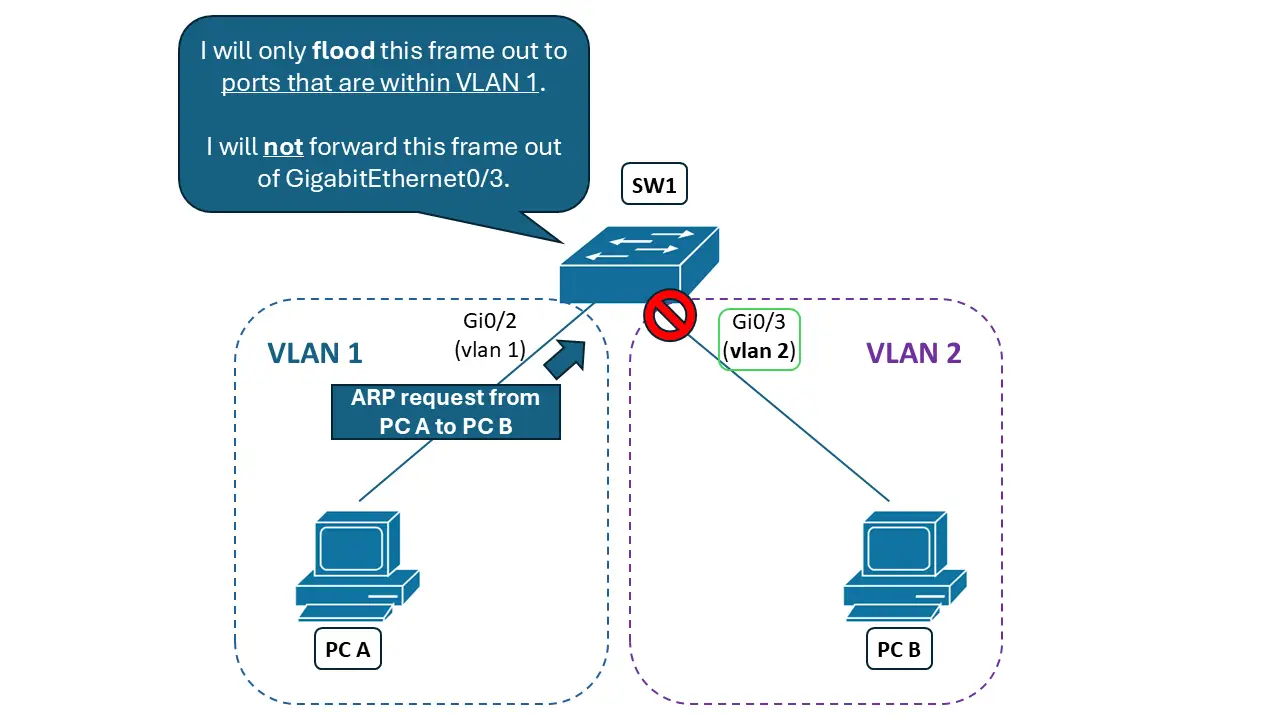
However, if we were to create a new VLAN on SW1 (VLAN 2) and moved PC B into that VLAN, PC A and PC B would never be able to communicate with each other directly, because they would not be able to complete ARP.

PC A in VLAN 1 sends an ARP request into switch SW1 via port Gi0/2. SW1 states it will only flood the frame to ports within VLAN 1 and will not forward it out Gi0/3, so PC B in VLAN 2 on Gi0/3 does not receive it, shown by a blocked icon between the VLANs.
PC A and PC B same switch different vlan
Achievable
 

They would both have to be in the same VLAN to communicate directly. Either VLAN 1 or VLAN 2.

Scenario 2 spanning across multiple switches

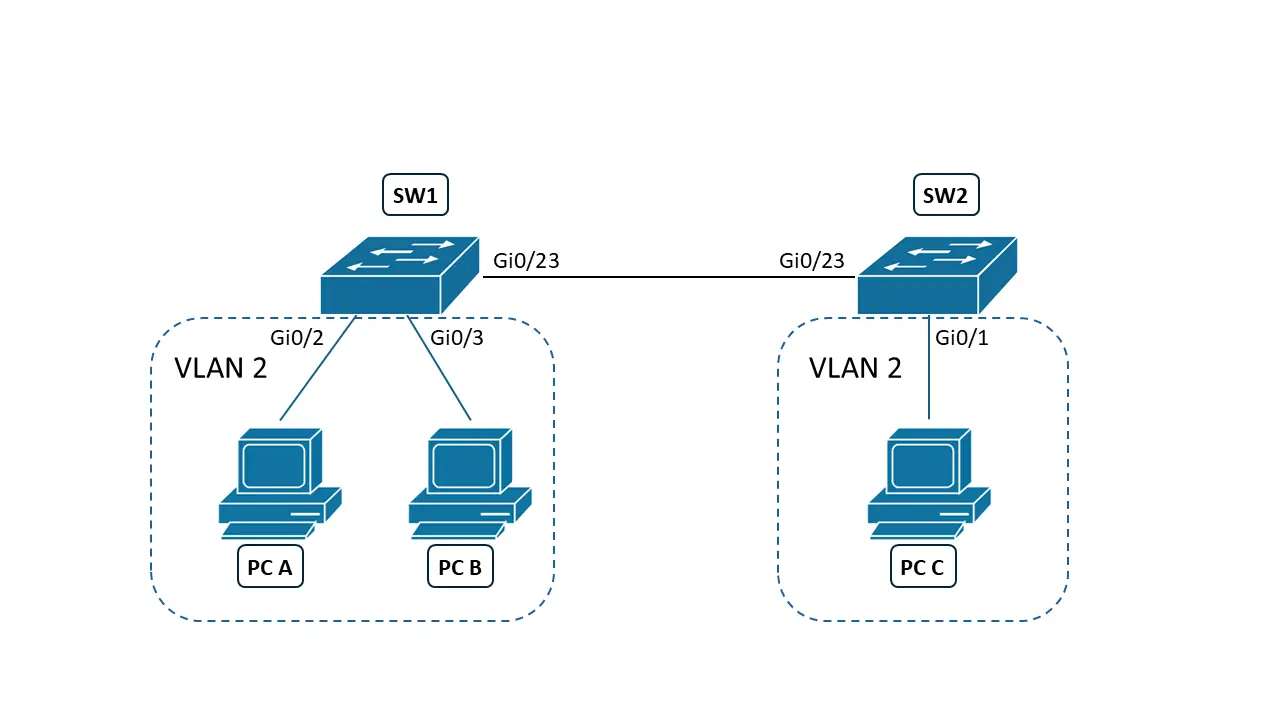
In another scenario, suppose Switch 1 is connected to Switch 2, and another host (PC C) is connected to Switch 2 in the same VLAN, which is a non-default VLAN. Let’s say that PC A, PC B and PC B have had their ports moved into VLAN 2.

SW1 (ports Gi0/2 and Gi0/3, both VLAN 2) connects to PC A and PC B, and links via Gi0/23 to SW2, whose Gi0/1 port (also VLAN 2) connects to PC C.
SW1 with PC A and PC B SW2 with PC C same vlan
Achievable
 

Would PC C on Switch 2 be able to communicate with PC A and PC B on Switch 1, given they are in the same VLAN?

(spoiler)

No.

The “why” comes from a principle you just saw.

By default, all ports on a Switch are in VLAN 1 , the Default VLAN

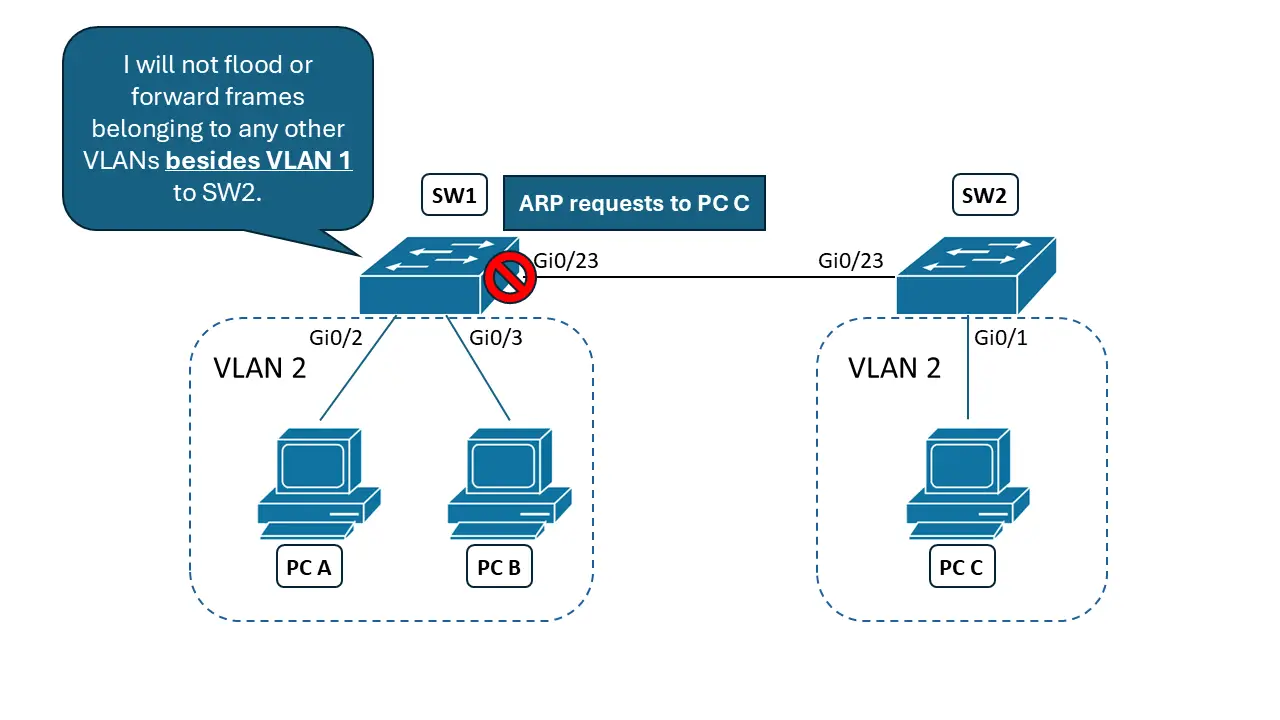
PC A and PC B can’t communicate with PC C because the link between Switch 1 and Switch 2 (their GigabitEthernet 0/23 ports) hasn’t been modified. It’s still configured in VLAN 1.

Meanwhile:

  • PC A and PC B on Switch 1 (GigabitEthernet 0/2 and GigabitEthernet 0/3) are configured in VLAN 2.
  • PC C on Switch 2 (GigabitEthernet 0/1) is also configured in VLAN 2.

Broadcasts only propagate within the VLAN they originate from. That means ARP Requests from PC A and PC B (in VLAN 2) can’t cross the inter-switch link, because the inter-switch ports (GigabitEthernet 0/23 on both switches) are still in VLAN 1 and therefore can’t send or receive VLAN 2 traffic.

So:

  • PC C never receives the ARP Requests.
  • PC A and PC B never learn PC C’s MAC address.
  • PC A and PC B can’t build Ethernet frames destined for PC C.
SW1 and SW2 connect via trunk links Gi0/23, but a blocked icon shows SW1 refusing to forward ARP requests to PC C. SW1's speech bubble states it will not flood or forward frames for any VLAN besides VLAN 1 to SW2, so PC A and PC B in VLAN 2 on SW1 can't reach PC C in VLAN 2 on SW2.
Inter-switch link cant forward non-default vlan frames
Achievable

Broadcasts and Switch Behavior

  • Switches flood broadcast frames out all ports except the receiving port (after learning source MAC)
  • Every host receiving a broadcast must interrupt CPU to process it, even if not the intended recipient
  • Large LANs suffer performance issues from excessive broadcast traffic

VLANs and Broadcast Domains

  • VLAN = Virtual LAN; segments a switch’s ports into separate Broadcast Domains
  • Default: all switchports belong to the same broadcast domain (same LAN)
  • Broadcasts in one VLAN cannot reach another VLAN
  • Modern use: VLANs primarily serve security/segmentation, not just CPU protection
  • VLAN 1 is the Default VLAN — cannot be created, modified, or deleted
  • To segment: (1) create VLAN, (2) move switchport(s) into it

MAC Address Table & VLANs

  • MAC table entries include both VLAN number and port where address was learned
  • “VLAN 1” entries indicate ports still on factory default settings

Intra-VLAN Communication Requirements

  • ARP relies on broadcasts, so it only works within the same VLAN
  • Hosts in different VLANs cannot complete ARP and thus cannot discover each other’s MAC addresses directly
  • Cross-VLAN communication requires a router or Layer 3 switch (covered in later routing chapters)

Multi-Switch VLAN Scenario — Trunk/Inter-switch Link Pitfall

  • Inter-switch links must be configured in the correct VLAN for traffic to cross switches (solution for multiple VLANs traversing a single link is discussed in the next chapter)
  • If the inter-switch port remains in VLAN 1 (default) while endpoints are moved to VLAN 2, VLAN 2 traffic (including ARP broadcasts) cannot cross the link
  • Result: hosts in the same VLAN on different switches fail to communicate if the connecting link isn’t properly configured for that VLAN

Sign up for free to take 10 quiz questions on this topic

Previous
Next  | 2.4.1 Link redundancy and the need for Spanning-Tree (STP)
All rights reserved ©2016 - 2026 Achievable, Inc.

Virtual LANs (VLANs)

In the previous chapter, you learned how hosts discover the MAC address of the host they want to communicate with. They do this by sending an ARP Request in a broadcast frame. If the target host is online and connected to the LAN, it responds directly (unicast) to the sender with an ARP Reply that includes its MAC address.

Broadcasts are useful when you don’t know where a host is on the LAN. They also help switches learn which switchport a host is connected to. However, broadcasts come with an important drawback.

Imagine a very large LAN made up of many interconnected switches, with endpoint devices connected to most (or all) switchports.

What happens when a switch receives a broadcast frame (after learning the source MAC address)?

(spoiler)

The switch makes copies of the broadcast frame and floods it out of every port, except the port on which the frame was received.

This can significantly impact network performance. It also affects endpoints that receive these broadcast copies. Broadcasts are meant for everyone, so every host that receives a broadcast frame must interrupt its CPU (Central Processing Unit) to process the frame. Even if the IP packet inside the frame isn’t destined for that device’s IP address, the device still has to examine and process the frame.

On a large LAN with hundreds or thousands of endpoints, repetitive broadcasts can become a serious burden because every endpoint receives and processes every broadcast frame.

To address this, Ethernet switches introduced a feature that lets you group physical switchports into separate LANs called “Virtual LANs,” or VLANs.

Virtual LANs (VLANs)

A VLAN segments the broadcast boundary. The area in which broadcasts can propagate is called a Broadcast Domain.

By default:

  • All ports on a switch are in the same broadcast domain.
  • That means they’re all on the same LAN.

When you connect one switch to another, you extend the LAN and also extend the broadcast domain.

When you create a VLAN and move switchports into it, those switchports become part of a different broadcast domain. As a result:

  • Broadcasts propagated within one VLAN can’t reach another VLAN.
  • Broadcasts originating within a particular VLAN can only be seen or received by hosts within that same VLAN.

In short; “VLANs segment Broadcast Domains”

Historically, VLANs were especially helpful because endpoint CPUs were more sensitive to periodic broadcasts due to hardware limitations at the time. Modern CPUs are much more capable, but excessive broadcasts can still cause problems.

Today, VLANs are commonly used as a security and segmentation tool: they separate groups of endpoints so only the intended devices can communicate directly and receive each other’s broadcasts.

By default, all switchports are in the Default VLAN, which is VLAN 1. It’s important to know that you cannot create, modify or delete VLAN 1.

If you want to group endpoints into different VLANs, the steps are:

  1. Create the VLAN
  2. Move the switchport(s) into the new VLAN

This process is straightforward. The key detail to remember is that switches associate learned MAC addresses with:

  • the switchport they were learned on, and
  • the VLAN that switchport is configured to be in.

Take the MAC address table example below. Notice that each MAC address entry includes a VLAN and the port where the MAC address was learned. That VLAN value tells you which VLAN the port belongs to.


Whenever you see “VLAN 1,” that means the switchport is still using its default factory settings and hasn’t been moved into an administratively created VLAN.

Always remember: hosts can only learn the MAC addresses of other hosts within the same VLAN only. That’s because hosts use ARP to discover MAC addresses, and ARP relies on broadcast frames. Since broadcasts from one VLAN can’t reach another VLAN, hosts in a different VLAN never receive the ARP Request and therefore can’t reply.

This doesn’t mean hosts can’t communicate across VLANs. They can, but they need a router (or a Layer 3 switch that can perform routing). We’ll cover that in the routing chapters (IP connectivity).

Let’s take a look at how intra-VLAN communication works in two scenarios:

Scenario 1: Hosts that are connected to a single switch

If two hosts are connected to the same switch and their ports are configured in the same VLAN, they can communicate directly.

However, if we were to create a new VLAN on SW1 (VLAN 2) and moved PC B into that VLAN, PC A and PC B would never be able to communicate with each other directly, because they would not be able to complete ARP.


They would both have to be in the same VLAN to communicate directly. Either VLAN 1 or VLAN 2.

Scenario 2 spanning across multiple switches

In another scenario, suppose Switch 1 is connected to Switch 2, and another host (PC C) is connected to Switch 2 in the same VLAN, which is a non-default VLAN. Let’s say that PC A, PC B and PC B have had their ports moved into VLAN 2.


Would PC C on Switch 2 be able to communicate with PC A and PC B on Switch 1, given they are in the same VLAN?

(spoiler)

No.

The “why” comes from a principle you just saw.

By default, all ports on a Switch are in VLAN 1 , the Default VLAN

PC A and PC B can’t communicate with PC C because the link between Switch 1 and Switch 2 (their GigabitEthernet 0/23 ports) hasn’t been modified. It’s still configured in VLAN 1.

Meanwhile:

  • PC A and PC B on Switch 1 (GigabitEthernet 0/2 and GigabitEthernet 0/3) are configured in VLAN 2.
  • PC C on Switch 2 (GigabitEthernet 0/1) is also configured in VLAN 2.

Broadcasts only propagate within the VLAN they originate from. That means ARP Requests from PC A and PC B (in VLAN 2) can’t cross the inter-switch link, because the inter-switch ports (GigabitEthernet 0/23 on both switches) are still in VLAN 1 and therefore can’t send or receive VLAN 2 traffic.

So:

  • PC C never receives the ARP Requests.
  • PC A and PC B never learn PC C’s MAC address.
  • PC A and PC B can’t build Ethernet frames destined for PC C.
Key points

Broadcasts and Switch Behavior

  • Switches flood broadcast frames out all ports except the receiving port (after learning source MAC)
  • Every host receiving a broadcast must interrupt CPU to process it, even if not the intended recipient
  • Large LANs suffer performance issues from excessive broadcast traffic

VLANs and Broadcast Domains

  • VLAN = Virtual LAN; segments a switch’s ports into separate Broadcast Domains
  • Default: all switchports belong to the same broadcast domain (same LAN)
  • Broadcasts in one VLAN cannot reach another VLAN
  • Modern use: VLANs primarily serve security/segmentation, not just CPU protection
  • VLAN 1 is the Default VLAN — cannot be created, modified, or deleted
  • To segment: (1) create VLAN, (2) move switchport(s) into it

MAC Address Table & VLANs

  • MAC table entries include both VLAN number and port where address was learned
  • “VLAN 1” entries indicate ports still on factory default settings

Intra-VLAN Communication Requirements

  • ARP relies on broadcasts, so it only works within the same VLAN
  • Hosts in different VLANs cannot complete ARP and thus cannot discover each other’s MAC addresses directly
  • Cross-VLAN communication requires a router or Layer 3 switch (covered in later routing chapters)

Multi-Switch VLAN Scenario — Trunk/Inter-switch Link Pitfall

  • Inter-switch links must be configured in the correct VLAN for traffic to cross switches (solution for multiple VLANs traversing a single link is discussed in the next chapter)
  • If the inter-switch port remains in VLAN 1 (default) while endpoints are moved to VLAN 2, VLAN 2 traffic (including ARP broadcasts) cannot cross the link
  • Result: hosts in the same VLAN on different switches fail to communicate if the connecting link isn’t properly configured for that VLAN

More from Administering Ethernet LANs

  • Wired network access